AdFection Turns Targeted Ads Into A Zero-Click Spyware Path
Citizen Lab traced Candiru spyware infections at Al Jazeera through targeted ads, exposing ad auctions as a precision zero-click delivery layer.
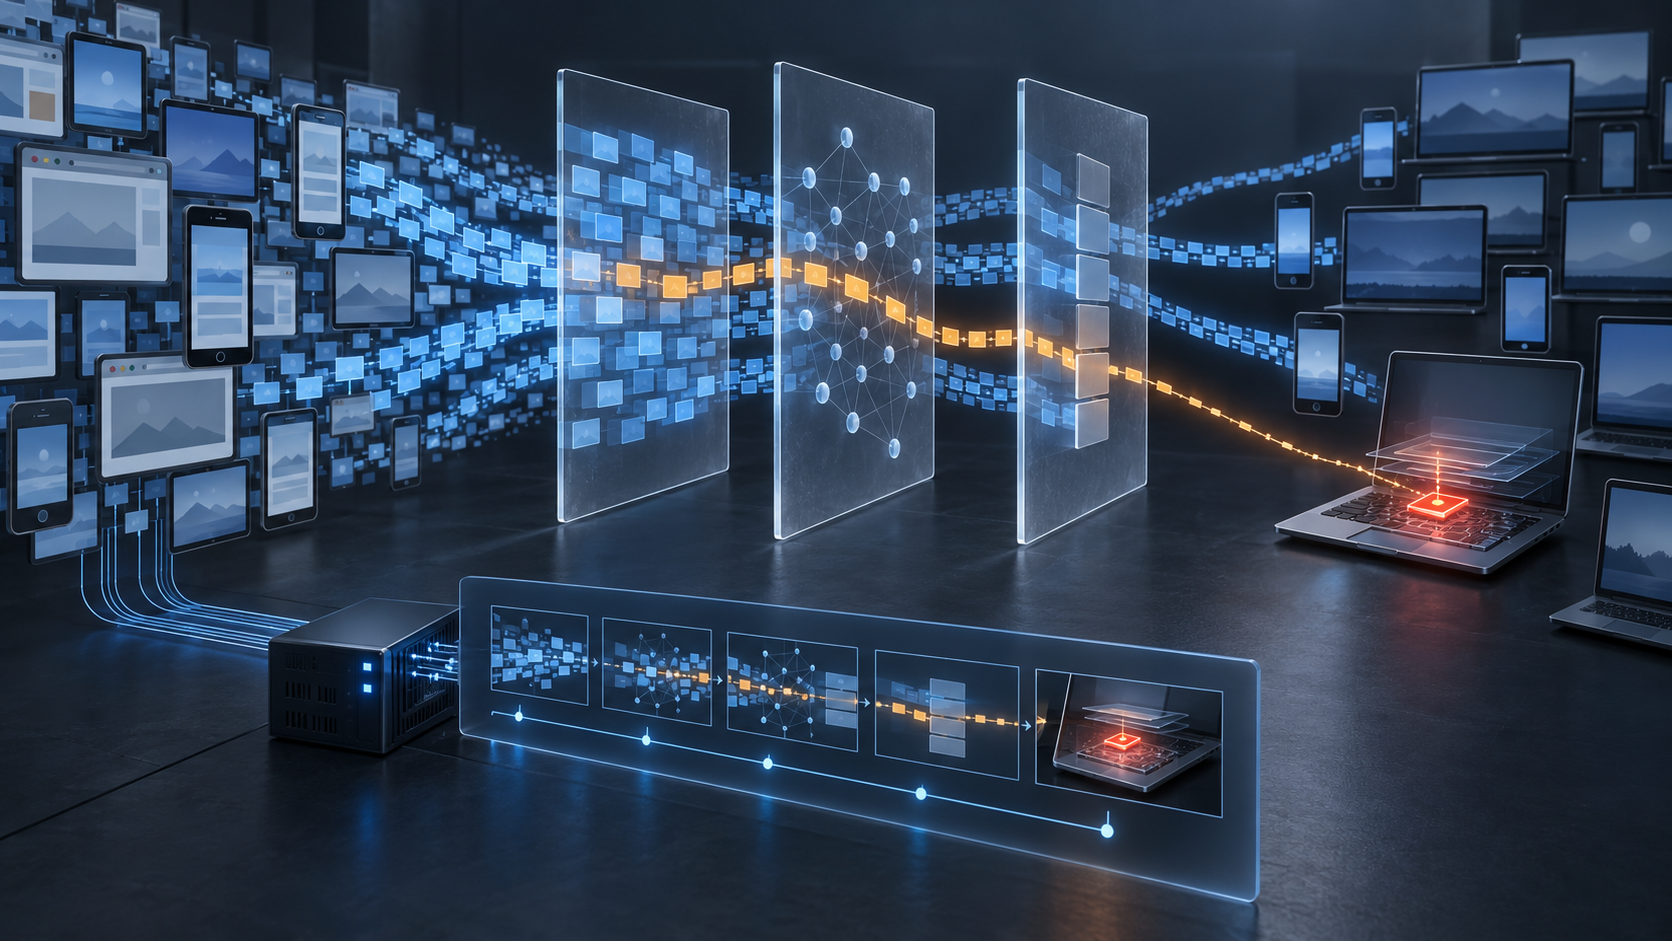
Citizen Lab published technical evidence on October 15 that targeted online advertisements were used to deliver zero-click mercenary spyware to devices at Al Jazeera. The researchers call the technique AdFection and link the recovered implant to Candiru with high confidence. Network logs from 2024 and 2025 show at least 45 Al Jazeera devices moving from a Discover-Tech ad impression to a Candiru validator and then command-and-control infrastructure. A recovered Windows DLL provided additional code and infrastructure evidence. Citizen Lab says this is the first public technical confirmation of mercenary spyware infection through targeted ads.
The broader dataset is large but must be interpreted carefully. Citizen Lab analyzed almost four billion Discover-Tech bidding records and found ad impressions across nearly 200,000 websites and mobile apps. An impression proves that an ad reached a device or network, not that the device was selected, exploited, or infected. Citizen Lab and Confiant describe a system that gathered identifiers and fingerprints at scale, then returned code only for selected targets. Google and several advertising vendors cut off Discover-Tech after disclosure. For high-risk organizations, the immediate response is to block ads and tracking at devices and gateways, disable mobile advertising identifiers where policy permits, keep browsers and operating systems current, and retain DNS, proxy, endpoint, and ad-request telemetry for investigation.
Key Takeaways
- check_circle Citizen Lab confirmed targeted-ad delivery in the Al Jazeera cases through network timing, infrastructure fingerprints, and a recovered Windows implant attributed to Candiru with high confidence.
- check_circle At least 45 Al Jazeera devices were targeted in 2024 and 2025, but the public report does not identify the government customer or publish a complete exploit chain.
- check_circle Discover-Tech's ad system could collect advertising identifiers, cookies, public IPv6 addresses, and device characteristics before deciding whether to return executable code.
- check_circle Almost four billion bid records and impressions across nearly 200,000 sites and apps show distribution reach, not an equivalent number of compromises.
- check_circle Google, IAB Europe, Beeswax, Eskimi, and Vungle took different forms of access-removal or suspension action after the researchers disclosed their findings.
- check_circle Ad and tracker blocking reduces this delivery surface, but patching, endpoint telemetry, incident response, and protection of high-risk personal devices remain necessary.
An Ad Impression Became The Trigger
Real-time advertising creates a delivery decision in fractions of a second. A website or app requests an ad, intermediaries exchange bid and device data, and the winning creative is rendered in a browser or embedded mobile frame. Code can accompany the image or video. Citizen Lab reports that Discover-Tech used this normal structure to place a script that called back to its infrastructure with an advertising identifier and network or device information.
Most viewers did not receive the next stage. Citizen Lab says the server could return an empty response when a device was not selected. For an eligible target, the same request could return JavaScript or direct the device toward additional infrastructure. This selective behavior limits exposure of the malicious content to scanners and reviewers while the ordinary ad-auction system supplies reach, identity signals, and repeated chances to encounter a chosen device.
The important control boundary is therefore not the click. The report says an ad could render visibly, in the background, or inside an app. The user did not need to follow a link. The public evidence supports zero-click infection in the investigated Al Jazeera cases, but it does not mean every ad can compromise every current device. Successful infection still depends on a selected target and an exploit chain compatible with the software it reaches.
The Al Jazeera Evidence Uses Several Independent Links
Al Jazeera provided network logs from the 2024 and 2025 attack period. Citizen Lab found a repeatable sequence: a device contacted Discover-Tech infrastructure during an ad impression, then reached a Candiru validator used to check the device, and finally communicated with Candiru command-and-control servers. At least 45 devices showed targeting. The newsroom also isolated a Windows DLL from one compromised device.
The recovered sample contained hardcoded command-and-control servers that matched the researchers' server fingerprint. Citizen Lab compared its persistence, a distinctive repeating XOR obfuscation method, and a hardcoded connectivity check with a Candiru chain captured in 2021. It concludes with high confidence that the DLL is a newer Candiru build. That attribution is a research assessment supported by multiple technical similarities, not a statement from Candiru or an identified government operator.
An important gap remains. Citizen Lab and Confiant did not recover the browser or application exploit that moved from ad-supplied code to operating-system compromise. Confiant captured a sophisticated JavaScript staging framework capable of detailed fingerprinting, encrypted command polling, and operator-supplied code execution within its current context. The Al Jazeera logs and implant establish the start and end of the path, but public reporting does not disclose every link between them.
Advertising Scale Is Not An Infection Count
Citizen Lab found a Discover-Tech server exposing almost four billion bidding records covering a four-month period in 2026. Those records placed the company's ads across close to 200,000 unique websites and Android or iOS apps in dozens of countries. Confiant separately assessed that related cookie-matching infrastructure produced billions of audience touchpoints each month. These figures show how much reconnaissance and delivery opportunity the advertising ecosystem can provide.
They do not show billions of victims. A bid can be lost, an impression can be benign, a callback can return no code, and a device can be unsuitable for exploitation. Citizen Lab explicitly says an ad impression on a sensitive network does not by itself confirm targeting or spyware infection. References to government, military, critical-infrastructure, media, or international-organization networks in the bid data should be treated as investigation leads, not breach notifications.
The confirmed Al Jazeera set is also carefully worded. At least 45 devices were targeted, and the report says devices at the network were infected. It does not publish an infection count for every targeted device, name the government customers behind the operation, or establish that every organization receiving a Discover-Tech impression was selected. Keeping those boundaries intact prevents a serious finding from turning into an unsupported global compromise claim.
The Ad Supply Chain Supplied Precision And Cover
Citizen Lab reconstructed a Discover-Tech platform called Controlium from exposed frontend source and authentication records. The researchers say it let partners define targets using advertising identifiers and network information, schedule controlled ads, and supply code for selected devices. The ad creative could submit cookies, a public IPv6 address, user-agent details, and other identifiers. That combination helps match a known person or device to an otherwise routine auction event.
Confiant observed a staged framework beginning with Discover-Tech's ad-serving domain and handing selected sessions to infrastructure it associates with Candiru. The JavaScript gathered device, network, rendering, and interaction characteristics, created encrypted channels, and polled for instructions. It could compile and execute operator-provided JavaScript with the authority of the frame or page context. Confiant also observed ad code reading first-party cookies where publisher integration made them accessible, including some live session identifiers and identity data not protected by HttpOnly.
Selective responses are also an evasion control. Eskimi told Citizen Lab that the tags returned different code based on device, IP address, location, and narrow targeting lists, helping them pass third-party verification. Confiant found decoy comments, obfuscation, encrypted results, and alternate transports. Traditional creative scanning asks what an ad does in the scanner's session. This system could make the more useful question whether the scanner was ever allowed to see what a chosen target would receive.
Cutting Off One Buyer Does Not Remove The Pattern
Citizen Lab says Discover-Tech had appeared on Google's certified-vendor and IAB Europe's approved-vendor lists since 2020 and bought inventory through several large platforms. After disclosure, Google terminated access to its exchanges, IAB Europe removed the company from its registry, Beeswax removed it from its buying platform, Eskimi blocked its accounts and domains, and Vungle paused access for review. Those actions reduce the documented operator's reach.
They do not change the underlying design. Real-time bidding still distributes granular device and audience data across many intermediaries, advertising identifiers remain useful for matching a device over time, and creatives can execute third-party code inside browsers and apps. A future operator does not need the same names, domains, or user interface to reproduce the mass-reconnaissance and narrow-delivery model.
Publishers and ad platforms therefore need controls beyond a static vendor list. Partner due diligence should include ownership and personnel review, continuous creative behavior testing from diverse devices and networks, limits on third-party script and identifier access, retention of bid and decision logs, and rapid cross-platform revocation. Cloaked creatives should be tested against differential responses, not cleared because one automated fetch looked benign.
High-Risk Organizations Need An Ad Exposure Plan
Citizen Lab recommends blocking advertising and tracking on work devices and at the network gateway, opting managed mobile devices out of ad targeting, using browsers with effective anti-tracking controls, and scrutinizing traffic associated with ad impressions. NSA guidance has long treated unnecessary advertising content as a malware surface and describes network and host-based blocking options. The new finding raises the stakes from common malvertising to selective mercenary surveillance.
Blocking must cover more than desktop browser extensions. Apps can embed ad software, personal phones may enter sensitive environments, encrypted DNS can reduce resolver visibility, and a commercial VPN's ad blocking may not see every application path. Use mobile-device management to reset or disable advertising identifiers where supported, define whether work data can be accessed from unmanaged devices, keep browsers and operating systems patched, and consider gateway controls that apply consistently to web and application traffic.
For investigation, preserve DNS, proxy, firewall, endpoint, browser, and mobile telemetry with synchronized timestamps. Compare ad-domain contact with subsequent validator or command-and-control activity and inspect endpoints showing that sequence. Do not wait for a user to report a suspicious click. If a journalist, executive, dissident, researcher, or other high-risk person may have been selected, involve a qualified spyware response team, isolate evidence carefully, and protect their contacts and sources while the device is examined.
Checklist
- Identify staff and personal devices with elevated surveillance risk, including journalists, executives, researchers, legal teams, activists, and people working in sensitive locations.
- Block advertising and known tracking infrastructure at managed endpoints and network gateways, then test coverage in browsers and ad-supported mobile apps.
- Disable or regularly reset mobile advertising identifiers through device policy where supported, and restrict targeted advertising on managed accounts.
- Keep operating systems, browsers, webviews, and common apps current so a targeted delivery path has fewer usable exploit chains.
- Retain synchronized DNS, proxy, firewall, endpoint, browser, mobile, and ad-request evidence outside the endpoint being investigated.
- Treat a Discover-Tech impression as a lead rather than proof of infection; look for the full sequence and obtain expert forensic help for high-risk cases.
- Require ad-tech vendors and publishers to preserve bid and creative-decision records, test cloaked differential behavior, and support rapid partner revocation.
Sources
- Citizen Lab: Exposing AdFection technical investigation and recommendations open_in_new
- Confiant: Discover-Tech ad-code and targeting analysis open_in_new
- Al Jazeera: Network statement and account of the spyware investigation open_in_new
- Microsoft: Earlier Candiru and DevilsTongue technical analysis open_in_new
- NSA: Blocking unnecessary advertising web content open_in_new
- U.S. Commerce Department: 2021 Entity List additions including Candiru open_in_new
Continue Reading
Atlassian File Access Turns Configuration Secrets Into Identity Risk
An exploited Atlassian Data Center flaw reads known files without authentication, exposing configuration secrets that can become administrative access.
BeyondTrust Zero-Day Turns Remote Support Into A Lateral-Movement Path
A BeyondTrust Remote Support zero-day gave an espionage actor an appliance foothold, persistent root access, and a path to managed endpoints.
AhsayCBS Exploitation Makes A Clean Rebuild The Recovery Path
Attackers chained two AhsayCBS flaws for SYSTEM access. Earlier fixes were incomplete, and compromised backup servers need a clean rebuild.