Gyazo Breach Turns Image Metadata Into A Long-Lived Privacy Risk
Gyazo's final investigation links unsafe media conversion to database exfiltration, 23.62 million user records, and metadata for deleted images.
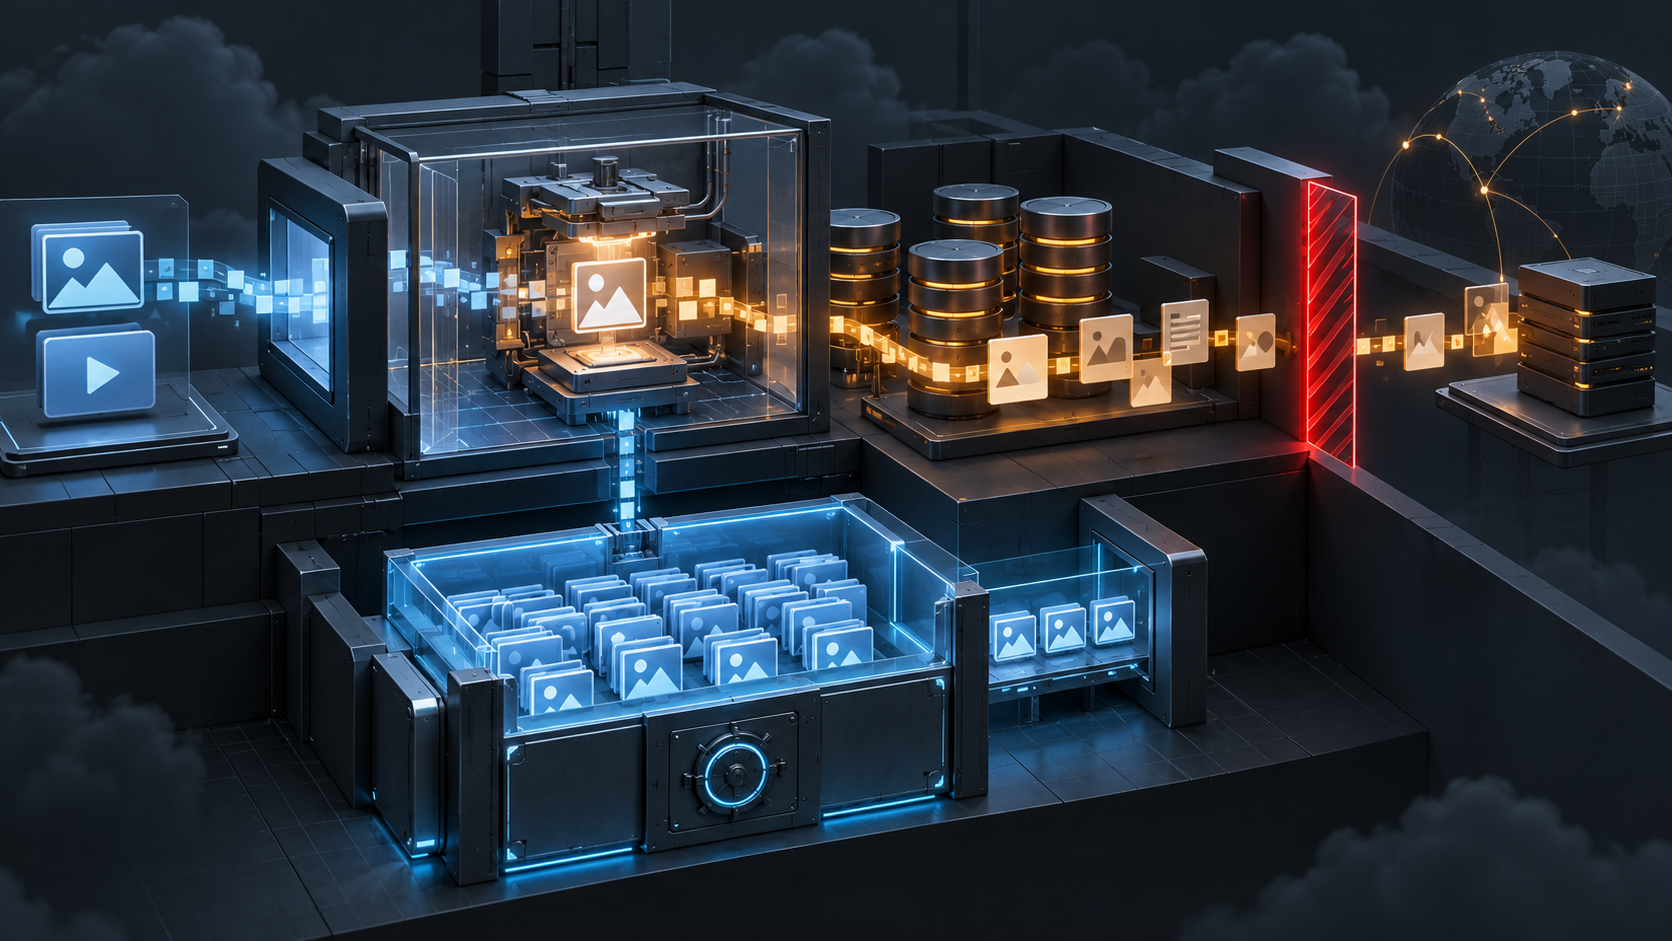
Helpfeel's final Gyazo investigation says a third party exploited unsafe handling of externally supplied values in an image-upload server's video and content conversion process. The values could be interpreted as commands, giving the intruder arbitrary command execution on the conversion server. From there, the intruder reached a database, performed large reads, and transmitted a large volume of data to an external server between September 11 and the early hours of September 12, 2026.
The confirmed scope includes about 23.62 million user records, about 490 million image-metadata records, a separately filtered set of about 2.4 million metadata records, about 174 million records tied mainly to deleted images or deleted accounts, and 432 image files belonging to 133 users. Missing content-level egress logs prevent a field-by-field reconstruction of everything transmitted. Users should change reused passwords, review pre-incident images before restoring delivery, and treat exposed image IDs, OCR text, locations, source IPs, and deleted-image metadata as durable privacy data rather than harmless indexing material.
Key Takeaways
- check_circle Helpfeel attributes the intrusion to its own content-conversion code, not a third-party component or supply-chain provider, and says externally supplied values could be executed as server commands.
- check_circle The conversion server could connect to the affected database, turning a media-processing flaw into access to user and image metadata at a much larger scale.
- check_circle The 23.62 million records are accounts, not necessarily unique people; about 18.01 million lacked a registered email address and about 5.62 million had one.
- check_circle Exposed metadata can include image IDs used to construct URLs, upload IP addresses, User-Agent strings, EXIF locations, OCR text, titles, source URLs, and hashed private-image passphrases.
- check_circle Helpfeel confirmed access to 432 image files across 133 users, but found no record of bulk image-file acquisition and no record that deleted image files themselves were obtained.
- check_circle The company is moving deleted-image metadata to a 60-day deletion policy, while its old practice retained that metadata for abuse investigations and responses to authorities.
The Final Report Establishes The Intrusion Path
Helpfeel detected suspicious behavior on the evening of September 11 and says it had blocked the identified route and terminated unauthorized connections by the early hours of September 12, then fixed the vulnerability later that day. On September 14, it confirmed unauthorized disclosure from the Gyazo database and stopped all image delivery. The company later invalidated authentication-related material, temporarily suspended the service, commissioned external forensic work, and resumed Gyazo on September 27 after additional checks.
The October 21 final notice adds the technical cause that earlier disclosures lacked. Part of the processing used to convert uploaded videos and other content did not safely handle values controlled from outside the system. Those values could be interpreted as commands on the conversion server. The intruder used that capability to execute unauthorized processes, explore the internal environment, connect from the server to an accessible database, read data at scale, and send data to a specific external server.
Helpfeel explicitly says the incident was not caused by outside software or a third-party service provider. Its current account places the defect in a system it developed and operated. It says no further access through the same paths has been confirmed after containment and no evidence was found that the intruder reached other systems or installed persistent malware. Those are bounded findings from the available investigation, not proof that every transient action was recorded.
A Conversion Worker Became A Database Route
Media conversion deserves the same distrust as any file parser exposed to the internet. A service may accept a screenshot, GIF, or video as data, but conversion often invokes complex libraries and helper processes, reads metadata, writes temporary files, and creates new output formats. In this case, Helpfeel says the flaw was command interpretation rather than a vulnerable external codec. The practical result was the same security-boundary failure: untrusted upload input crossed into operating-system execution.
The second boundary was reachability. Command execution on the conversion host became a breach of far more than the current upload because that host could connect to a database containing user records and historical metadata. Helpfeel says it has since strengthened access controls between internal systems and encrypted internal communications, and is reviewing system design to minimize damage after an intrusion. Encryption in transit protects against network observation; it does not by itself stop a compromised, authorized workload from querying a database.
A safer architecture treats conversion as disposable and narrowly privileged. The worker should not hold general database credentials, should receive only the object it must transform, and should write output through a constrained broker or object-store role. Network egress should be restricted to expected destinations, temporary storage should be isolated, and the process should run without shell access where the conversion pipeline permits it. The incident record does not specify Gyazo's redesigned topology, so these are general controls, not claims about completed product changes.
The Record Counts Describe Different Kinds Of Exposure
The user table contained about 23.62 million account records. Helpfeel says roughly 18.01 million, or 76 percent, belonged to anonymous users without a registered email address, while about 5.62 million had an email address. Depending on the account, fields could include names or nicknames, email addresses, password hashes, user and device IDs, login session IDs, X integration tokens, Google SSO email addresses, profile data, login times, subscription and billing status, and usage statistics. Payment-card numbers and other payment method information were not included.
The image-related sets are separate. About 490 million metadata records were associated mainly with images uploaded in or before January 2019, representing about 14.4 percent of all images. Another roughly 2.4 million records were retrieved through specific filters. About 174 million records related mainly to images deleted in or before February 2023 or to accounts deleted by then. These numbers are metadata records, not a count of image files or unique people, and overlap should not be inferred without data the company has not published.
The fields make the exposure operationally meaningful. An image ID can help construct a direct image URL. OCR text can contain messages, credentials, customer names, or internal tickets that never appeared in an account profile. EXIF can disclose location, upload IPs can associate activity with a network, and source URLs can reveal where a capture came from. A hashed passphrase is not a plaintext password, but weak passphrases may still warrant caution when the verification material is available to an attacker.
Metadata Exposure Is Not The Same As Bulk Image Theft
The forensic evidence supports a careful distinction. Logs showed large database reads and a large outbound transfer from the same server, leading the external specialists to assess a reasonably high likelihood of exfiltration. The environment did not record the actual content of those outbound communications, so the investigation could not directly prove every transmitted field or final record count. The listed data scope combines that forensic assessment with Helpfeel's own investigation.
For image files, the result is narrower. Helpfeel found no record of bulk acquisition and no record that image files corresponding to deleted images were obtained. Its additional investigation did confirm that the intruder viewed or obtained 432 files belonging to 133 users, who were notified individually. The company also says it cannot completely exclude access to other images through URLs present in the leaked metadata. That residual risk explains why pre-incident delivery remains disabled until an owner reviews and restores it.
No confirmed misuse, impersonation, financial loss, or other secondary harm had been identified as of October 20. Helpfeel says it has monitored illicit marketplaces since late September and had not found the data there, with monitoring planned for at least a year. Absence from monitored markets is useful but incomplete evidence. Private sharing, direct targeting, and future use would not necessarily produce a public sale listing.
Users Need To Review Visibility And Account Risk Separately
Helpfeel says the exposed password-related field was a one-way password hash rather than plaintext, and that it invalidated certain authentication and integration material. It nevertheless asks users who have not changed their Gyazo password since the incident to do so, and to change the same or similar password on other services. That advice remains sound because invalidating sessions or tokens does not change an exposed reusable password hash, and the public notice does not specify the hash algorithm or cost needed to estimate offline resistance.
Image delivery requires a different decision. Images uploaded before the intrusion remain owner-only by default, with Gyazo Teams members able to view team material subject to its existing setting. A user can restore individual images, a selected group, or all images. Restoration returns the previous visibility, including anyone-with-the-link access. Review the content and permission of sensitive screenshots individually rather than using bulk restoration as a convenience step.
Treat incident-themed email as a phishing surface. Helpfeel says its notifications about affected deleted-image metadata will not ask recipients to follow a link or take action on a linked site, and it will not request a password or credit-card number for the incident. Navigate directly to Gyazo, verify notices in the service interface, and use the published contact channel if a message claims urgent account action.
Deleted Data And Missing Egress Detail Are Design Findings
Gyazo's old process deleted image files after a period but retained associated metadata for abuse investigations and responses to authorities. The final notice says Helpfeel will automatically delete metadata 60 days after an image is deleted, progressively remove older deleted-image metadata where legal and reporting duties permit, establish retention periods for deleted-account operational records, and publish retention policies. The breach shows why deletion semantics must name every layer: object, metadata, derivative, index, log, backup, and account link.
The investigation also exposes a telemetry gap. Helpfeel could correlate large reads with large outbound volume but could not reconstruct the transmitted content. Its planned measures include longer log retention and stronger anomaly detection for database access and external transfer. Useful controls include query-level attribution to workload identity, alerts for bulk reads outside normal jobs, destination-aware egress records, and tamper-resistant off-host logs. Logging should record enough structure to investigate without creating a second store of sensitive content.
Helpfeel says it reviewed the whole Gyazo codebase, fixed other high-severity issues, strengthened internal access controls, and plans external assessments, continuous static analysis, a security operations center, and secure-development training. Those commitments are material, but the final notice does not publish the exact vulnerable parameter, exploit payload, database permissions, hashing scheme, complete exfiltrated field set, or independent report. Users and corporate customers should base immediate action on the confirmed scope while tracking future disclosures for those unresolved details.
Checklist
- Change the Gyazo password if it has not been changed since September 11, and replace the same or a similar password everywhere else it was used.
- Review pre-incident images before restoring delivery, checking both the content and the previous visibility setting; avoid bulk restoration for sensitive screenshots.
- Treat image IDs, OCR text, EXIF locations, upload IPs, titles, source URLs, and deleted-image metadata as exposed privacy data when assessing personal or corporate risk.
- Verify incident messages through the Gyazo service or Helpfeel's published contact channels; do not follow links in mail claiming to be a deleted-image notification.
- For workplace use, identify secrets, customer data, support tickets, infrastructure details, and internal conversations captured in Gyazo, then rotate or remediate anything still actionable.
- Community and product operators should isolate media conversion, remove database access from workers that do not need it, restrict egress, and log bulk reads under distinct workload identities.
- Define deletion across files, metadata, derivatives, indexes, logs, backups, and deleted accounts, with documented retention periods and evidence that scheduled deletion runs.
Sources
- Helpfeel: Gyazo final investigation results, October 21, 2026 open_in_new
- Helpfeel: first Gyazo breach notice and affected data fields open_in_new
- Helpfeel: second Gyazo notice and deleted-image metadata scope open_in_new
- Helpfeel: Gyazo service resumption and image delivery controls open_in_new
- Gyazo Help: user actions and breach FAQ open_in_new
- Helpfeel: Helpfeel and Cosense system-boundary assessment open_in_new
Continue Reading
Zeabur Breach Turns Environment Variables Into A Full Rebuild Problem
Zeabur says attackers read 3.2 million environment-variable records and reached 101 servers as root. Customers need secret rotation, rebuilds, and migration.
PHP2Shell Exploitation Turns Runtime Patching Into Incident Response
Two PHP runtime flaws allow unauthenticated code execution. Fix the runtime, restart every worker, and investigate activity from at least October 17.
eMudhra Key Compromise Exposes The Gaps In Certificate Revocation
Eight eMudhra intermediate CA keys were recoverable from public data. Browsers blocked them, but custom trust stores and certificate chains need review.