AOMEI Update Tampering Turns Minutes Into A Supply-Chain Blind Spot
Attackers briefly altered AOMEI update infrastructure to deliver CROSSROAD and SHINYROAD, leaving endpoints compromised after servers looked normal again.
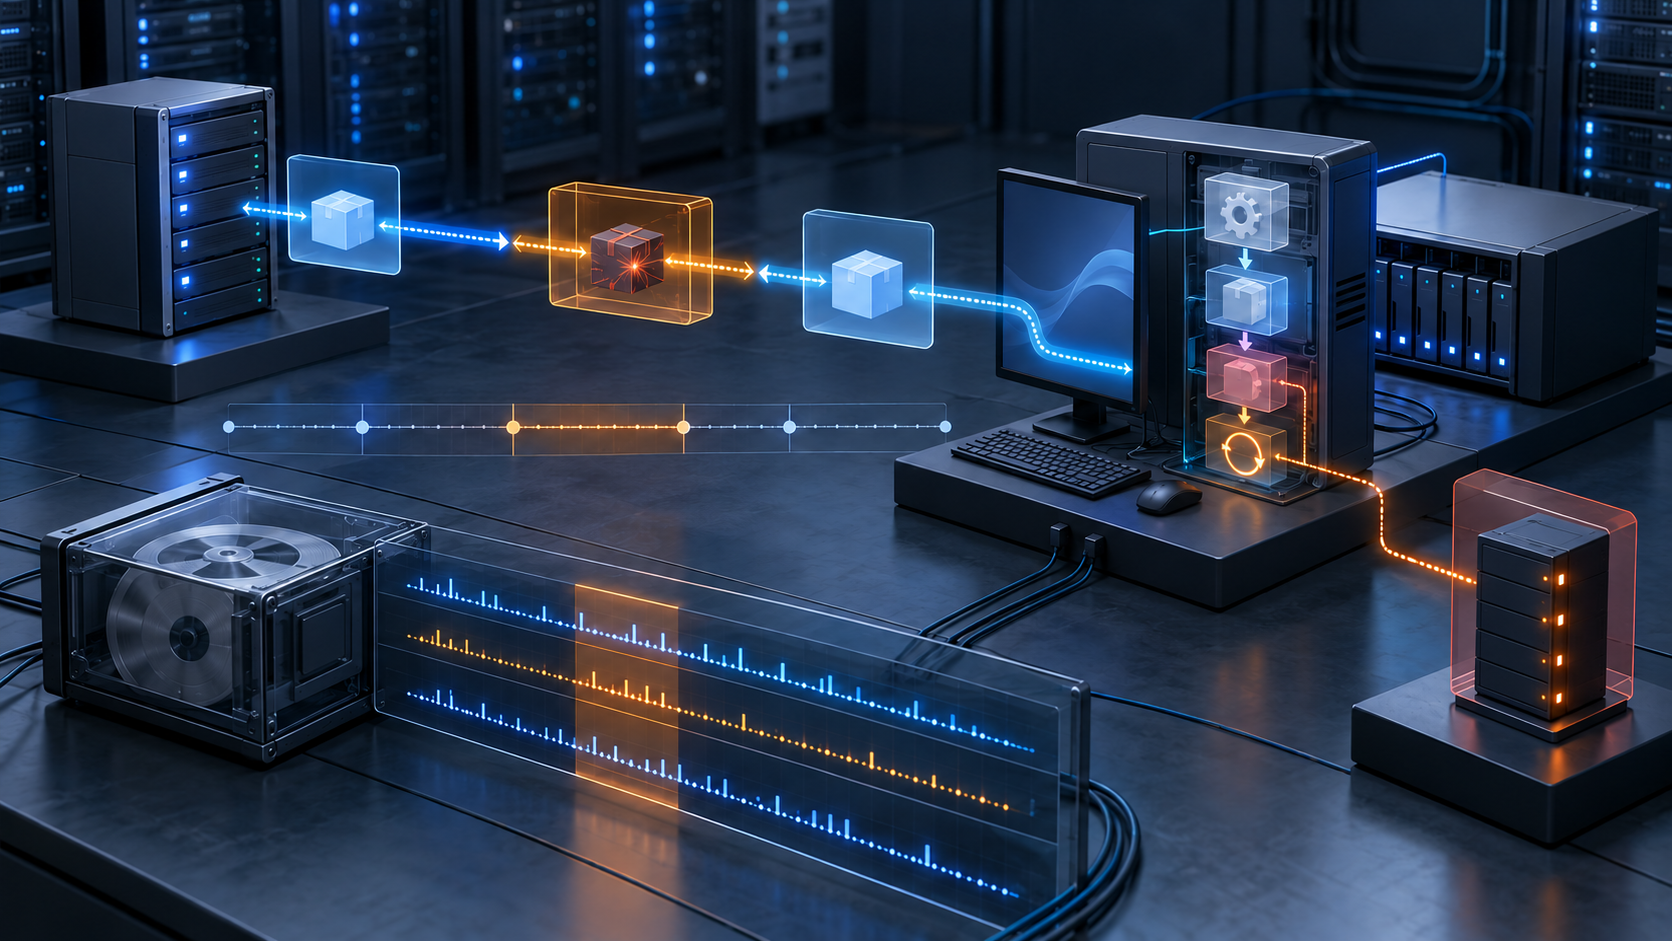
Google Threat Intelligence Group and Mandiant disclosed a supply-chain campaign that tampered with AOMEI Technology update infrastructure between April and July 2026. The actor, tracked as UNC7017, changed update and notification configuration on AOMEI origin servers for only five to ten minutes at a time. Systems that checked during those windows received malicious instructions; checks immediately before or after returned authentic content. Google says the campaign delivered the CROSSROAD downloader and SHINYROAD backdoor, while ManageEngine's METAL team traced the first confirmed endpoint chain through AOMEI Backupper's normal in-application content path.
A current clean server, current vendor download, or upgraded client cannot prove that an endpoint missed an earlier window. CROSSROAD restored local configuration, deleted artifacts, established scheduled-task persistence, and staged follow-on components. A July wave also used a one-pixel WebDAV resource to coerce NetNTLMv2 authentication. AOMEI told Mandiant on July 29 that corrective actions had been taken, but Google explicitly warns that server-side remediation does not disinfect endpoints. Organizations need deployment inventory, historical EDR and proxy review, published indicator hunting, credential scoping, and trusted endpoint recovery.
Key Takeaways
- check_circle UNC7017 repeatedly changed AOMEI-hosted update and notification configuration for five to ten minutes, then restored authentic content, creating a narrow but real infection window.
- check_circle The updater trusted an MD5 value delivered inside the same unauthenticated configuration that supplied the package URL, so the attacker could redirect the file and replace its expected checksum together.
- check_circle ManageEngine observed AOMEI Backupper's local WebView automatically launch the bundled executable without exploiting a software vulnerability and without an extra user click beyond the application running.
- check_circle CROSSROAD validated the environment, reverted local update settings, self-deleted artifacts, created scheduled persistence, and staged SHINYROAD or other remote-access components.
- check_circle The July 20 configuration also forced a hidden WebDAV request to an attacker-controlled address, creating a separate path for NetNTLMv2 credential exposure.
- check_circle AOMEI reported corrective server action, but endpoint clearance requires historical hunting and remediation; version 8.5.0 availability does not establish that an older installation was never compromised.
Short Tampering Windows Defeated Snapshot Checks
Google and Mandiant place the campaign between April and July 2026 and say directly observed server modifications lasted only five to ten minutes. Confirmed windows included ten minutes on May 28, six minutes on July 16, and five minutes on July 20. Malware samples and related telemetry extend the visible activity back to late April, and the researchers assess that additional windows probably escaped observation.
The delivery result depended on timing. A client that requested the configuration while tampering was active received a malicious package location and execution instructions. The same request before or after the window returned legitimate AOMEI content. ManageEngine reproduced the normal flow in a lab after investigating two affected customer endpoints and found nothing malicious, then continued because its endpoint telemetry showed the original process chain.
This pattern breaks a common triage shortcut. Fetching the URL now, checking its current certificate, or rescanning the present configuration only describes current state. It does not reconstruct what an endpoint received months earlier. Historical endpoint, DNS, proxy, firewall, and content-capture data become primary evidence.
The Trusted Updater Carried Its Own Replacement Trust Record
AOMEI Backupper and AnyViewer use an ABMarket flow in which background processes request two configuration files over HTTPS. down_html.ini supplies the available version, package URL, and expected MD5 value. Notifycfg.ini controls in-application notices and can specify local commands or programs. Under normal conditions, these files point to AOMEI-hosted content.
UNC7017 changed both sides of that control path. During the July 16 window, it replaced the package URL, incremented the minor build value, and supplied the MD5 for the malicious archive. It also expanded the notification configuration with more than 35,000 repetitive sections, overriding normal version checks so the client would trigger the download and execute the unpacked CROSSROAD loader.
The MD5 check did not provide independent authenticity because the same unauthenticated configuration named both the file and its expected digest. The attacker did not need to find a collision. It replaced the package reference and the comparison value together. Transport encryption protected the client-to-server connection, but the trusted server-side configuration itself had been altered.
A Local Notification Path Became Code Execution
ManageEngine's endpoint record showed ABNotify.exe processing a 232-file promotional bundle. The included upgrade-now.html created a link to a sibling upgrade-now.exe and clicked it programmatically. Because Notifycfg.ini loaded the page from a local file path inside AOMEI's rendering directory, the embedded WebView handed the executable to the system shell. The chain used intended content-handling behavior rather than a separate browser or WebView vulnerability.
No additional user interaction was required while the application was running. That makes the process ancestry more useful than the apparent package name. An unsigned executable launched by ABNotify.exe from an AOMEI html directory is not a normal software update merely because the parent path is trusted. ManageEngine published a Sigma rule for this parent-child pattern and reports no known legitimate executable launches from the rendering hierarchy.
The actor also varied infrastructure. Early payloads used Alibaba Cloud Object Storage, July activity moved to vendor-themed storage-data.com hosts, and the July 20 initial package came from a public Google Cloud Storage bucket before later stages used attacker domains. Blocking only newly registered domains would miss the cloud-hosted first step.
CROSSROAD Cleaned The Scene While SHINYROAD Stayed
CROSSROAD was the initial downloader and environment gate. It checked its path for the AOMEI name, queried public services to identify the system's external address and country, avoided its main payload path for systems geolocated to China, and used a global mutex to prevent duplicate execution. It also looked for selected security products and could halt in environments likely to expose the chain.
The loader then worked against forensic reconstruction. Google says it restored the local update URL and build value to the legitimate defaults, removed temporary files, and could self-delete. It created the RadminComponentRuntime scheduled task to launch a follow-on process every three hours. An administrator inspecting the current configuration could therefore see the correct vendor URL while persistence and payload components remained elsewhere on the host.
The follow-on tooling mixed legitimate and malicious components. ManageEngine observed the genuine Radmin Server installer, but did not find evidence that Radmin itself was running. Remote access instead depended on an attacker DLL side-loaded by a legitimate launcher, which registered an encrypted PocketPy implant inside dllhost.exe. Google also links campaign infrastructure to Adaptix command-and-control components and tracks the modular backdoor as SHINYROAD.
The July Wave Added A Credential Boundary
On July 20, the modified notification file replaced a legitimate promotional banner with a one-by-one-pixel window that requested a file URL through WebDAV from 8.210.84.56. The hidden request could cause Windows to transmit a NetNTLMv2 challenge-response value to the attacker-controlled system without visible user interaction.
That is separate from the malware package path and expands the response beyond file hashes. Teams should review outbound SMB and WebDAV exposure, authentication telemetry, and use of the affected endpoint's account during and after the window. A captured NetNTLMv2 value is not a plaintext password, but it can support offline cracking or relay in environments where protocol and signing controls allow it.
Google recommends blocking the published storage-data.com hosts and IP addresses, restricting outbound TCP 445 and external WebDAV, and searching for the Anyviewer-loader/1.0 and Anyviewer-ipcheck/1.0 user agents. Those indicators are valuable pivots, not a complete campaign boundary. The actor changed staging services, and short windows may have used infrastructure that investigators did not observe.
Server Repair Does Not Clear Historical Endpoints
Mandiant notified AOMEI on July 17 and says the vendor responded on July 29 that corrective actions had been taken. AOMEI's public changelog now lists Backupper 8.5.0, released October 9, and its support documentation offers automatic or manual upgrade paths. Neither page describes the incident or presents the new version as an endpoint disinfectant. Treat the latest installer as software maintenance, not retrospective proof of integrity.
Inventory every system that ran AOMEI Backupper or shared update components during the April-to-July period, including systems that are no longer online. Search historical process creation for ABNotify.exe launching executables from the html hierarchy, the RadminComponentRuntime task, published hashes and domains, side-loaded DLLs, suspicious dllhost.exe behavior, public IP lookup patterns, and outbound WebDAV or SMB. Preserve files and logs before cleanup because the loader intentionally removed or reverted artifacts.
Where the chain executed, isolate the host and recover from a trusted baseline. Scope the user and service identities active on it, review credentials and tokens stored or used there, and investigate adjacent systems reached after the suspected time. Updating, uninstalling, or reinstalling AOMEI alone does not remove an independent backdoor or undo credential exposure. The durable control is a monitored update boundary: signed configuration and artifacts, isolated testing, process-behavior alerts, egress limits, and retained telemetry long enough to reconstruct a five-minute event.
Checklist
- Inventory AOMEI Backupper, AnyViewer, ABMarket components, versions, install paths, execution accounts, and systems present from April through July 2026.
- Preserve historical EDR, process creation, DNS, proxy, firewall, SMB, WebDAV, scheduled-task, and authentication data before removing software or artifacts.
- Hunt for ABNotify.exe launching executables from an AOMEI html directory, the RadminComponentRuntime task, published hashes, side-loaded DLLs, and unusual dllhost.exe activity.
- Search for the published storage-data.com infrastructure, campaign IPs, cloud staging endpoints, Anyviewer user agents, and public IP lookup services in the reported chain.
- Block unauthorized outbound SMB and WebDAV, review NetNTLMv2 exposure and relay protections, and scope every account active on a suspected endpoint.
- Isolate and rebuild confirmed systems from a trusted source, then rotate exposed credentials and investigate downstream access rather than relying on an application reinstall.
- Require independent artifact and configuration authenticity, behavioral updater monitoring, staged release gates, egress controls, and historical telemetry for privileged desktop software.
Sources
- Google Threat Intelligence Group and Mandiant: ephemeral AOMEI supply-chain tampering open_in_new
- ManageEngine METAL: endpoint chain and AOMEI Backupper detections open_in_new
- Google Threat Intelligence Group: software supply-chain mitigation guidance open_in_new
- VirusTotal: GTIG collection of published campaign indicators open_in_new
- AOMEI: Backupper version history and current 8.5.0 release open_in_new
- AOMEI: automatic and manual Backupper upgrade paths open_in_new
Continue Reading
ConnectWise Cloud Backup Incident Turns App Trust Into Tenant Risk
Attackers abused ConnectWise application identities to enter Microsoft 365 tenants, where disabling the original apps may not remove added access paths.
Ivanti Zero-Day Chain Makes Memory Evidence Part Of VPN Response
An exploited Ivanti Connect Secure chain reached root, stole identity data, erased logs, and evaded disk-based integrity checks by operating in memory.
Atlassian File Access Turns Configuration Secrets Into Identity Risk
An exploited Atlassian Data Center flaw reads known files without authentication, exposing configuration secrets that can become administrative access.