Ivanti Zero-Day Chain Makes Memory Evidence Part Of VPN Response
An exploited Ivanti Connect Secure chain reached root, stole identity data, erased logs, and evaded disk-based integrity checks by operating in memory.
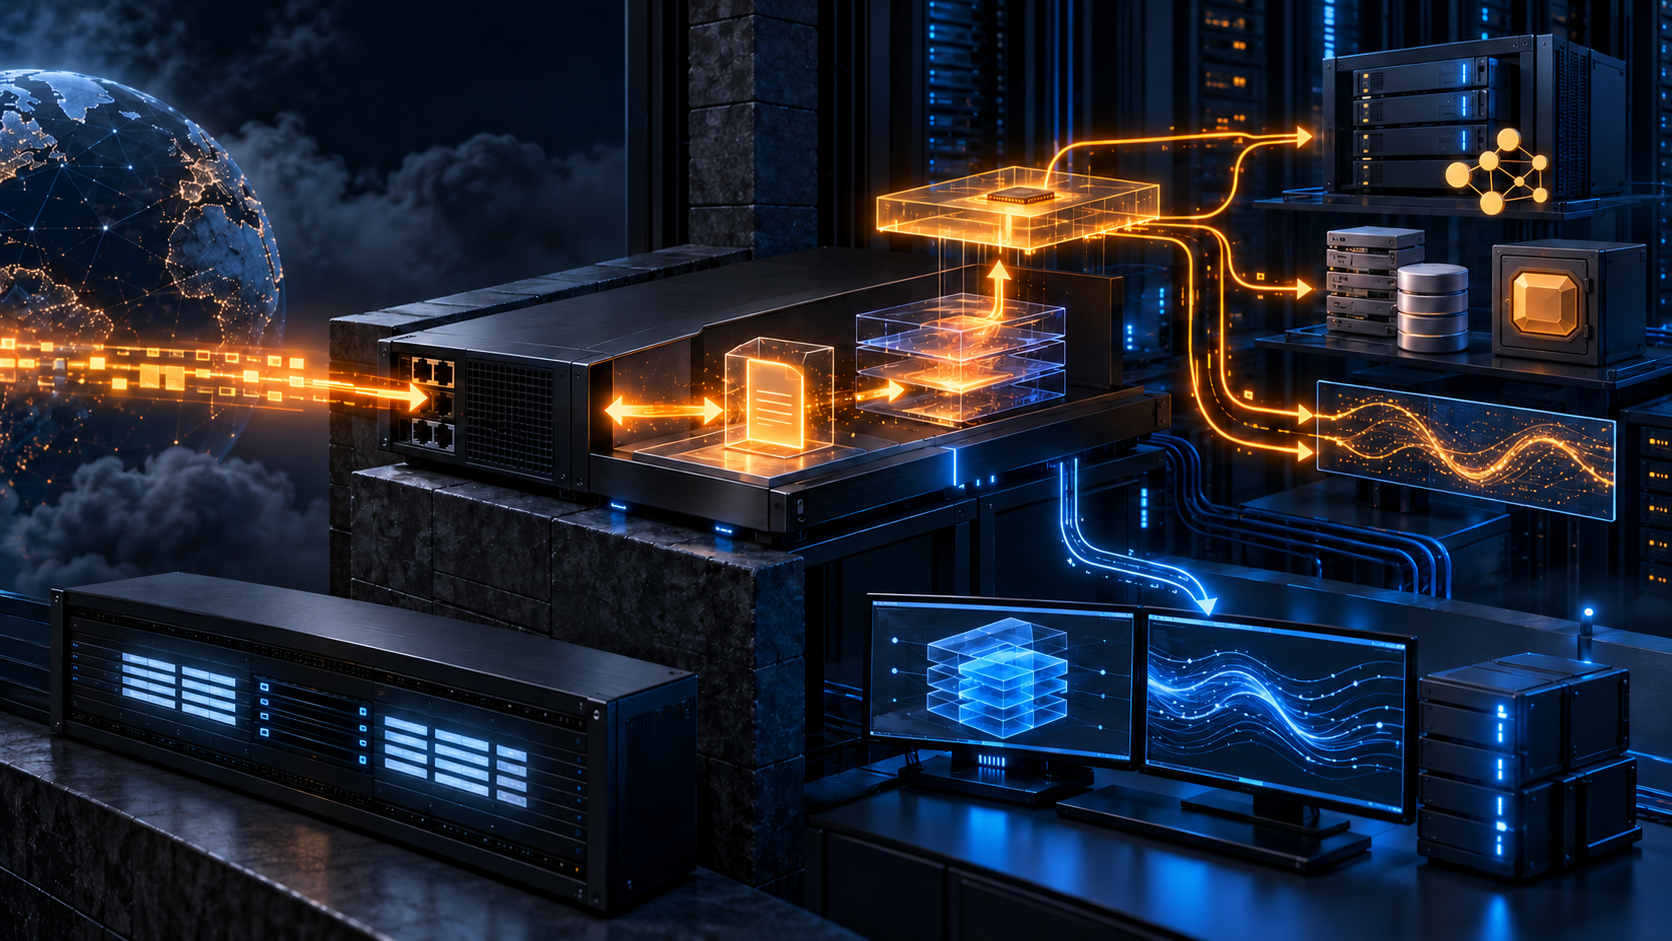
Ivanti and Volexity disclosed active exploitation of Ivanti Connect Secure on October 13. In the investigated case, a previously unknown actor chained an authentication bypass, a brief file-write and execution race, and a separate privilege-escalation flaw to run commands as root without logging in. Ivanti tracks the first two stages as CVE-2026-104935. The third stage is now identified as CVE-2026-111357. Volexity observed exploitation beginning October 3 against an appliance running 22.8R2.4, which was fully patched at the time.
The response problem is larger than installing the October update. The actor passed commands through repeated HTTPS exploitation, kept important stages in memory, restored modified state, and selectively removed local log entries. Volexity says the normal Integrity Checker Tool would not detect the in-memory changes in this chain. The actor also reached the appliance's identity boundary, collecting LDAP credentials, Active Directory metadata, authentication records, and material useful for LAPS, BitLocker, password spraying, and Kerberos attacks. Teams need the fixed CVE-2026-104935 build immediately, but they also need network, memory, identity, and off-appliance evidence before declaring the gateway clean.
Key Takeaways
- check_circle CVE-2026-104935 is an actively exploited authentication-bypass and command-execution path with a CVSS 3.1 score of 8.6; CISA added it to KEV on October 13 with an October 16 federal due date.
- check_circle Volexity reconstructed three zero-day stages: unauthenticated CGI routing, a transient file-write execution race, and a separate privilege escalation through the privileged dsinvoked service.
- check_circle Ivanti's fixed builds for the remote entry path include 22.8R2.5, 25.1.1.2, 25.1.3.0, and 25.1.3.1; 22.7R2.14 and earlier are listed as unaffected by CVE-2026-104935.
- check_circle CVE-2026-111357 covers the root-escalation stage. The public record on October 17 identifies exploitation but does not list a fix, so teams must track Ivanti's next release separately.
- check_circle The observed operator did not need a persistent webshell. It re-ran the chain for each command, restored memory and configuration changes, and deleted selected debug and audit events.
- check_circle Compromise scope includes identities and downstream systems because the gateway stored directory credentials, carried authentication traffic, and could query sensitive Active Directory attributes.
The Disclosure Followed An October Intrusion
Volexity began investigating suspicious activity on October 5 and traced the source to an Ivanti Connect Secure appliance. The device was running 22.8R2.4 build 19097, the current patched release at the time. Forensic reconstruction found repeated exploitation beginning October 3. Ivanti published its advisory and fixed releases on October 13, while Volexity published the incident analysis the same day.
Ivanti says a limited number of customers were affected before disclosure. That statement establishes zero-day exploitation but does not provide a global victim count. Volexity's detailed account is based on one investigated environment and names the actor UTA0576. Its low-confidence assessment leans toward criminal motivation, but the ultimate objective was not determined because the activity was detected and disrupted. Neither the vendor nor the incident responder supports a broad attribution claim.
CISA added CVE-2026-104935 to the Known Exploited Vulnerabilities catalog on October 13 and set October 16 as the federal remediation deadline. The deadline has passed as of this report. It applies directly to federal civilian agencies, but the combination of confirmed exploitation, unauthenticated command execution, and an internet-facing identity gateway makes the same emergency priority reasonable elsewhere.
Three Stages Turned A Public Route Into Root
The first stage abused a disagreement inside the gateway's request handling. A public login-page route was allowed before authentication, while a separate request value selected a protected CGI handler as the actual destination. Volexity describes this as an authentication bypass: the access decision and the execution target were not bound to the same path.
The selected handler accepted an uploaded file, wrote it to a predictable temporary location, and only then checked whether it was a valid archive. An invalid upload was deleted, but a short interval existed between write and deletion. The actor sent parallel requests so the temporary script could execute during that interval. Ivanti groups this file-write and remote-execution behavior with the authentication bypass under CVE-2026-104935.
That execution initially ran as the lower-privileged cgi-server user. A third flaw targeted dsinvoked, a privileged service that reads task definitions from the shared DSCache configuration store. The exploit temporarily changed the in-memory library behavior used by the CGI process, redirected a maintenance task to an interpreter, and asked dsinvoked to run it as root. The newly assigned CVE-2026-111357 distinguishes this escalation step from the patched remote entry path.
The Fixed Build Closes The Remote Entry Path
The affected and fixed ranges need branch-level verification. Rapid7's reproduction of the vendor table lists 25.1.1.1 and earlier in that line as fixed by 25.1.1.2; 25.1.2.2 and earlier in that line as fixed by 25.1.3.0 or 25.1.3.1; and 22.8R2.4 and earlier in that line as fixed by 22.8R2.5. The CVE and NVD records list 22.7R2.14 and prior as unaffected by CVE-2026-104935. Administrators should compare the complete installed build, not only the major release label.
Applying a fixed CVE-2026-104935 release blocks the unauthenticated chain Volexity observed. It does not remove commands already run, restore deleted evidence, revoke stolen credentials, or answer whether the appliance was used to reach internal systems. It also does not fix CVE-2026-111357. That local escalation remains a separate exposure, although the known internet attack depends on first obtaining execution through the remote stages.
Organizations still on an affected build should isolate the appliance from both the internet and the internal network where operations permit, preserve volatile state, and upgrade through Ivanti's supported process. CERT-FR specifically warns that shutting down can destroy needed evidence. High-availability designs need an incident plan that can preserve the suspect node without silently shifting untrusted state or credentials to its peer.
A Clean Integrity Check Is Not Clearance
The observed operator avoided the artifact pattern many appliance playbooks expect. It did not install a first-stage backdoor or webshell. Instead, it repeated the exploit for each command and returned output through the same HTTPS response. The privilege stage patched a library in process memory, changed DSCache just long enough to invoke a root task, and then restored both the memory byte and task definition.
Volexity says Ivanti's Integrity Checker Tool looks for unexpected on-disk modifications and would not detect this in-memory manipulation. The actor also filtered selected entries from the Ivanti debug log and Linux audit log while retaining older records, which makes an apparently normal file and log set weak negative evidence. The tool remains useful for the changes it can find, but a clean result cannot exclude this chain.
Preserve RAM, core dumps, packet captures, external reverse-proxy or firewall logs, DNS, authentication records, VPN session history, and directory audit data before destructive recovery. Volexity recovered scripts, open files, process behavior, and packet-capture activity from memory. Network monitoring also exposed the mismatch between the public route and protected handler. These are independent evidence paths the attacker did not fully control.
The Gateway Became An Identity Collection Point
Post-exploitation moved quickly from the appliance to identity data. Volexity observed extraction of stored domain credentials, appliance configuration, authentication methods, and limited Active Directory metadata. The actor queried for LAPS local-administrator passwords, BitLocker recovery information, password-bearing directory attributes, and logon-script paths using the gateway's directory service account.
The appliance also provided a traffic vantage point. A renamed packet-capture utility watched protocols including plaintext LDAP and could recover credentials, HTTP Basic Authentication values, and NTLM challenge-response material. Volexity observed attempts to parse and exfiltrate existing capture data. It also found password spraying, Kerberos tooling, local DNS reconnaissance, and authentication-log review for valid usernames.
This makes response an identity and network investigation, not only a firmware task. Inventory every LDAP or Active Directory bind account, local administrator, API key, certificate, authentication integration, and service credential stored on or presented through the gateway. Review what each identity could read, when it authenticated elsewhere, whether new accounts or group memberships appeared, and whether password spraying or unusual directory queries followed the appliance activity.
Recovery Must Treat The Appliance As A Compromised Trust Broker
Where compromise is plausible, isolate and collect before resetting. CERT-FR recommends filesystem and memory snapshots for virtual appliances, evidence sequestration, the external Integrity Checker, and a factory reset for confirmed compromise. It also cautions that some threats can survive a reset in sensitive scenarios. Recovery should therefore follow Ivanti support guidance and an independently verified clean baseline, not an assumption that one reset button covers every persistence layer.
Rotate or reissue secrets in an order that prevents the recovered gateway from reintroducing risk. This includes LDAP and Active Directory service credentials, local and administrative passwords, API keys, authentication-server service accounts, Kerberos tickets, licensing credentials, client and server certificates, and TLS or code-signing certificates present on the device. Determine whether plaintext traffic or captured recovery material expands that list.
After reconnection, test the evidence pipeline. Confirm that gateway events, reverse-proxy requests, identity logs, DNS, firewall flows, VPN sessions, and configuration changes arrive off the appliance with synchronized time. Alert on unusual volume to public login routes, a mismatch between the requested route and backend handler, unexpected temporary scripts, packet-capture processes, and forwarding gaps. Track Ivanti's advisory for the CVE-2026-111357 fix and validate that every node crosses that second patch boundary when it becomes available.
Checklist
- Inventory every Connect Secure appliance, full build number, cluster peer, public endpoint, and authentication integration.
- Upgrade affected branches to 22.8R2.5, 25.1.1.2, 25.1.3.0, 25.1.3.1, or a later vendor-approved release, then verify the running build on every node.
- Preserve memory, core dumps, external logs, network flows, DNS, VPN sessions, directory events, and appliance storage before shutdown or reset.
- Use the Integrity Checker as one signal, not clearance; hunt for route-to-handler mismatches, temporary scripts, packet capture, log gaps, and the published Volexity indicators.
- Map and rotate LDAP or Active Directory binds, local accounts, API keys, certificates, Kerberos material, and other secrets stored on or crossing the gateway.
- Review Active Directory queries, password spraying, group changes, new accounts, LAPS or BitLocker access, and downstream authentication from the exposure period.
- Follow CVE-2026-111357 separately and deploy Ivanti's privilege-escalation fix across the cluster as soon as a supported release is published.
Sources
- Ivanti: Connect Secure advisory for CVE-2026-104935 open_in_new
- Volexity: chained exploitation, forensics, and indicators open_in_new
- CISA: Known Exploited Vulnerabilities catalog open_in_new
- NVD: CVE-2026-104935 affected versions and KEV deadline open_in_new
- CERT-FR: isolation, evidence, reset, and secret-rotation guidance open_in_new
- Canadian Centre for Cyber Security: October 16 update for CVE-2026-111357 open_in_new
Continue Reading
ConnectWise Cloud Backup Incident Turns App Trust Into Tenant Risk
Attackers abused ConnectWise application identities to enter Microsoft 365 tenants, where disabling the original apps may not remove added access paths.
AOMEI Update Tampering Turns Minutes Into A Supply-Chain Blind Spot
Attackers briefly altered AOMEI update infrastructure to deliver CROSSROAD and SHINYROAD, leaving endpoints compromised after servers looked normal again.
Atlassian File Access Turns Configuration Secrets Into Identity Risk
An exploited Atlassian Data Center flaw reads known files without authentication, exposing configuration secrets that can become administrative access.