Chainalysis Breach Makes Token Invalidation The First Recovery Boundary
Chainalysis says all users' password hashes and live tokens were exposed. Invalidate sessions, rotate API keys and verify every reconnect.
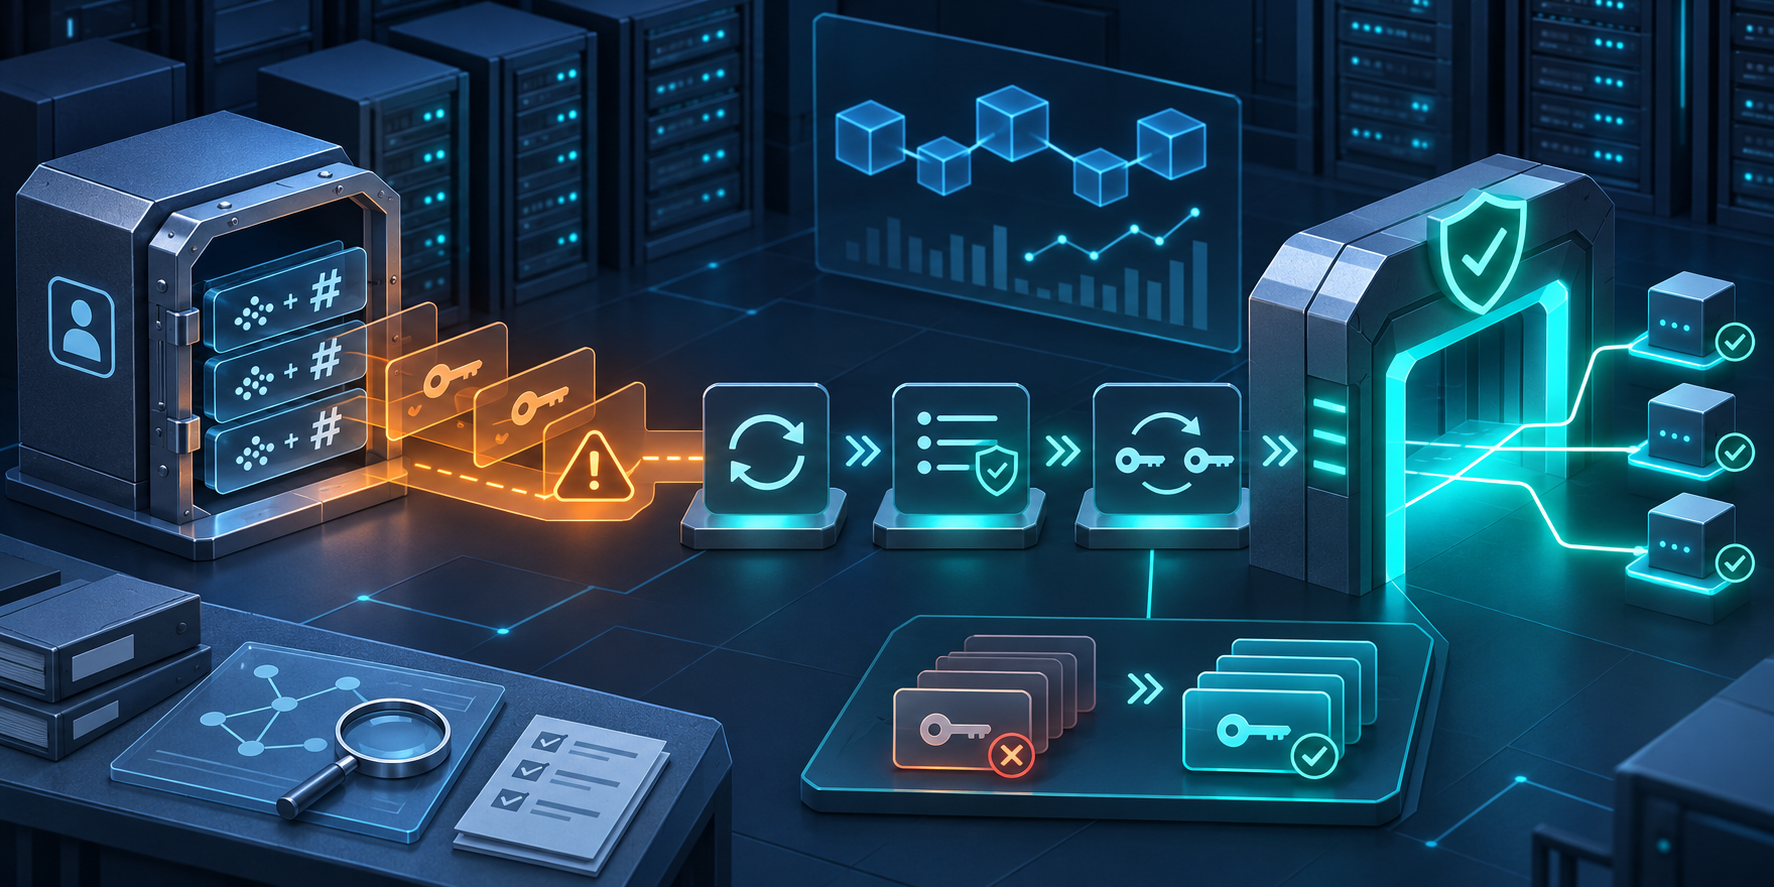
Chainalysis says a malicious actor obtained names, usernames, password hashes and live tokens for all users during a multifront incident involving its systems and internal tools. The company separately notified a subset of customers that passwords had been exposed in what it called an on-path attack. After detecting abnormal activity, Chainalysis took its login page, KYT interface and API, Address Screening, Reactor and Data Solutions offline in stages. It says Reactor, KYT and Address Screening returned on November 7 with enhanced controls and customer-specific reconnection instructions.
A password reset alone is not a complete response to a live-token exposure. Customers should preserve account, identity-provider, proxy, API and automation evidence; invalidate active sessions and other bearer material; rotate every Chainalysis API key from a trusted administrative path; and verify that old credentials fail before reconnecting transaction flows. Chainalysis says it has no evidence that investigation content was accessed or attribution data manipulated, but it has not defined the exposed tokens, published the access window or disclosed how many KYT accounts showed unauthorized activity. Those facts remain open, not negative findings.
Key Takeaways
- check_circle Chainalysis expanded its initial scope from customer profile information to password hashes and live tokens for all users as its investigation developed.
- check_circle A subset of customer passwords was exposed through an on-path attack, according to notices quoted in the company's incident page.
- check_circle The company detected abnormal KYT activity and says it is directly notifying customers whose accounts appear to have been accessed without authorization.
- check_circle Reactor, KYT and Address Screening were back online on November 7, but customers were told to reconnect through instructions sent directly by Chainalysis.
- check_circle Chainalysis has not publicly defined live tokens, so responders should not assume they were only browser sessions or only API credentials.
- check_circle The vendor reports no evidence of accessed investigation content or manipulated attribution data, while the investigation and customer notifications continue.
The Public Scope Changed As The Investigation Progressed
Chainalysis first said on October 30 that an external actor using what it described as offensive agentic techniques gained unauthorized access to systems and internal tools. At that point, the company reported access to user IDs, names, email addresses and organization role labels, while saying it had found no indication of exposed investigation content, transaction results, plaintext passwords, MFA secrets or session tokens. It also said the incident was unrelated to the Binance theft disclosed days earlier.
The operational response widened. On November 2, Chainalysis removed Reactor and Data Solutions while keeping transaction-monitoring products available under closer observation. On November 4, it told some customers that an on-path attack had exposed their Chainalysis password and locked those accounts pending a reset. Later that day it reported abnormal activity in KYT, took the KYT interface and API, Address Screening and the login page offline, and disclosed that names, usernames, password hashes and live tokens for all users had been exposed.
On November 6, the company began restoring KYT and Address Screening in phases behind trusted-IP allowlists, password resets and API-key rotation. Its November 7 update says Reactor, KYT and Address Screening are online again with enhanced security measures and asks customers to follow emailed reconnection instructions. The changing statements are not proof that an earlier disclosure was deceptive. They show why incident scope must be versioned by time and evidence rather than copied into a permanent conclusion on the first day.
Live Tokens Put Invalidation Ahead Of Password Rotation
A password proves knowledge during authentication. A live session or access token can represent the result of an earlier authentication and may continue authorizing requests until it expires or is rejected. That distinction changes response order. Resetting a password can stop new password-based sign-ins while leaving an already issued bearer token usable if the service does not revoke it. NIST IR 8587 treats token lifecycle controls, verification, monitoring and misuse resistance as separate security work rather than a side effect of password management.
Chainalysis has not said whether live tokens means browser sessions, API access tokens, refresh tokens, integration credentials or several types. It also instructs customers to rotate API keys, which may be a precaution or may reflect separately exposed automation credentials. Responders should keep those categories separate until the vendor provides a mapping. Treat the phrase as a minimum scope statement: at least one class of still-usable authorization object was exposed for all users.
Ask Chainalysis or the assigned account team which token and key classes existed for the organization, when each class was invalidated, whether invalidation covered every region and product, and what audit fields identify their use. Locally, revoke federated and application sessions where appropriate, rotate Chainalysis keys, and record old identifiers without preserving secret values in an ordinary ticket. A new password and MFA enrollment do not prove that an old API key or copied session has stopped working.
Product Outages And Data Findings Have Different Boundaries
Chainalysis removed products in stages for assessment and later for observed abnormal activity. Reactor supports investigations; Data Solutions supplies blockchain data; KYT and Address Screening support transaction and address risk workflows. Taking a product offline establishes containment or caution, not confirmed compromise of all data in that product. Conversely, returning a product to service establishes an operational recovery decision, not proof that every customer account and integration has been independently cleared.
The company says it has no evidence that investigation content such as graphs, notes or cases was accessed and no evidence that Chainalysis attribution data was manipulated. Those are useful negative findings because altered attribution or exposed cases could affect law-enforcement, compliance and fraud decisions. They should be preserved with the qualifier that they describe evidence available to Chainalysis during an ongoing investigation.
KYT has a different confirmed boundary. Chainalysis says it observed abnormal activity and is directly notifying customers whose KYT accounts appear to have been accessed without authorization. It has not published how many accounts, what actions occurred, whether the activity used the exposed live tokens or passwords, or whether transaction registration was modified. Customers should use their own account, network and downstream records to establish activity rather than treating either product downtime or the all-users exposure as a substitute for evidence.
Customer Recovery Needs A Credential And Evidence Matrix
Start with a matrix of every Chainalysis user, SSO identity, local password, MFA method, browser session, API key, service account, integration, trusted egress address and product entitlement. Mark which items Chainalysis has confirmed exposed, which it has instructed the customer to replace and which remain unknown. Preserve the vendor's notices, identity-provider sign-ins, authentication and proxy logs, outbound network records, API calls, SIEM alerts and application changes before reset activity overwrites useful context.
Use a trusted route to the service. Navigate directly to the known Chainalysis domain or contact the established account team rather than following an unexpected reset link. Submit allowlist addresses only through the channel specified in the verified customer instructions. Reset unique passwords, rotate API keys, re-enroll or verify MFA where the customer notice requires it, and end active sessions. If a Chainalysis password was reused elsewhere, change the reused copies too, beginning with email, identity administration and systems that can reset other accounts.
For every replaced secret, record issuer, owner, scope, creation time, last use, consuming service and revocation evidence. Test the old credential from a controlled path and require a denial. Then search for its identifier or associated account in the exposure window and after revocation. MITRE classifies stolen application access tokens as credentials that can authorize remote API actions with the user's or service's permissions, so investigation must follow the permissions actually attached to each token rather than the label on the account.
Reconnect Transaction Flows Without Restoring Stale Trust
KYT and Address Screening integrations may sit inside deposit, withdrawal, customer-onboarding and compliance workflows. An unplanned key replacement can therefore stop business processes or encourage a rushed rollback to a known-exposed credential. Build a controlled cutover. Create the replacement through the restored administrative path, place it in the approved secret store, update one consumer group, validate expected requests and risk responses, then expand while monitoring failures and unexpected source addresses.
Trusted-IP allowlisting can reduce reachable sources during recovery, but it is not identity. Inventory every real egress path, including NAT gateways, failover sites, workers and managed integration platforms, and exclude developer laptops or broad network ranges that do not need production access. Confirm how emergency changes will work if an egress address changes. Keep application credentials narrowly scoped even when the source address is allowed, and alert when a key appears from an unregistered network.
Do not delete the old key from evidence before documenting its identifier and last known use, but do remove it from runtime secret stores, deployment variables, runbooks and developer copies. OWASP's secrets guidance emphasizes inventory, rotation, revocation and audit across the lifecycle. Completion means the replacement works, the old key fails, all intended consumers have moved, unplanned consumers are identified, and transaction-registration behavior matches a known-good baseline.
Root Cause And Full Customer Impact Remain Open
The public incident page does not explain the on-path mechanism, the internal entry point, the systems from which password hashes and tokens were obtained, the hashing scheme, token types, exposure duration or total number of users. It does not connect the on-path password exposure, all-user token exposure and KYT abnormal activity into one confirmed technical chain. The phrase offensive agentic techniques describes the vendor's assessment of attacker methods, not a public root-cause analysis or attribution to a named group.
Chainalysis also has not published the number of KYT accounts accessed, actions taken through them, whether any API keys were confirmed used, or the expected return of every remaining service. Customers should track later reports for changes to those boundaries and keep their incident records updateable. A later finding of data access would not make today's careful negative finding wrong; it would change the evidence available.
The durable engineering lesson is to make token invalidation observable and fast. Maintain a complete token and service-account inventory, short lifetimes where the protocol allows them, narrow scopes, separate human and workload authority, source and behavior monitoring, and tested kill switches that do not depend on the compromised login path. NIST's incident-response guidance places recovery alongside continuous risk management. For a platform embedded in compliance decisions, customer recovery must restore both access and confidence in the identity and evidence behind each request.
Checklist
- Preserve every Chainalysis notice and the timeline of product access, lockout, restoration and local changes.
- Inventory users, sessions, SSO connections, MFA methods, API keys, integrations, products and trusted egress addresses.
- Invalidate sessions and tokens, reset unique passwords and rotate API keys through the verified restoration path.
- Confirm that every old password, token and API key fails while each intended replacement succeeds.
- Review identity, network, API and application evidence for unauthorized KYT or other product activity.
- Reconnect integrations in stages, monitor source addresses and remove stale secrets from every runtime consumer.
- Track Chainalysis updates for token types, root cause, access window, affected-account count and investigation-data findings.
Sources
- Chainalysis incident page: evolving scope, credential exposure, product response and November 7 restoration open_in_new
- NIST IR 8587: token verification, lifecycle controls, monitoring and misuse resistance open_in_new
- NIST SP 800-63B: authenticator invalidation, password and remote-authentication guidance open_in_new
- NIST SP 800-61 Rev. 3: evidence-led incident response and recovery planning open_in_new
- MITRE ATT&CK T1528: application access-token theft and resulting remote authority open_in_new
- OWASP Secrets Management: inventory, rotation, revocation and audit lifecycle open_in_new
Continue Reading
HestiaCP Fixes Put Every Tenant-To-Root Helper In Scope
HestiaCP 1.10.6 closes tenant-to-root paths in domain, backup, restore and SSH helpers. Patch, restrict the panel and investigate host state.
OpenAM 16.1.4 Makes Session And Federation Trust Explicit
OpenAM 16.1.4 fixes live-session disclosure and unsigned SAML paths to account takeover. Upgrade, invalidate sessions and test federation policy.
MetaMask Staking Incident Separates Rewards From Withdrawal Authority
MetaMask says an attacker redirected 0.385 ETH in validator rewards without reaching staked principal. Verify recipients, exits and withdrawal control.