MetaMask Staking Incident Separates Rewards From Withdrawal Authority
MetaMask says an attacker redirected 0.385 ETH in validator rewards without reaching staked principal. Verify recipients, exits and withdrawal control.
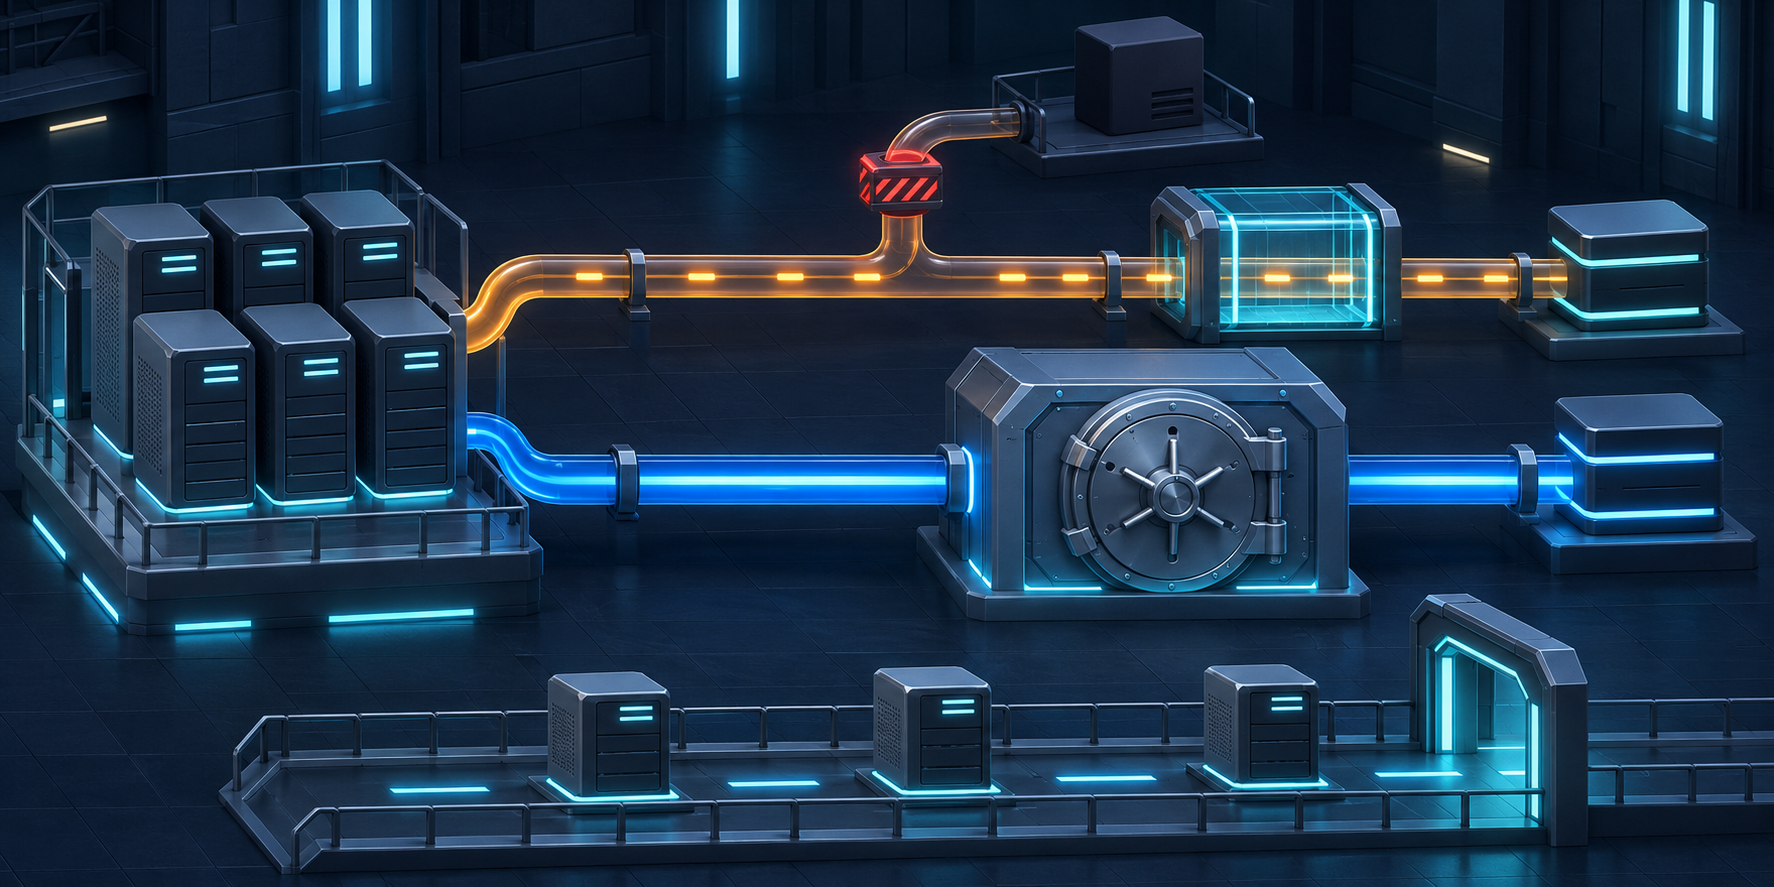
MetaMask says an attacker gained unauthorized access to part of its staking infrastructure on September 28 and briefly changed the execution-layer fee-recipient addresses for certain validators. Approximately 0.385 ETH in rewards was diverted before the change was identified and reversed that day. MetaMask reports no evidence that wallet infrastructure, Secret Recovery Phrases, private keys, withdrawal keys or customers' staked principal were compromised. It exited every affected validator as a precaution and reported on November 5 that those exits had completed.
The incident demonstrates why a validator's operating authority, fee recipient and withdrawal authority must be treated as separate controls. A fee-recipient change can redirect transaction tips and MEV from blocks proposed by a validator without changing the withdrawal credential that controls staked ETH and consensus-layer withdrawals. Affected staking customers should preserve validator identifiers, onchain recipient history and provider notices; follow direct instructions from MetaMask or their staking provider; and expect exit, sweep and reactivation delays. Ordinary MetaMask wallet users are not being asked to reset wallets or reveal recovery phrases.
Key Takeaways
- check_circle MetaMask identified unauthorized infrastructure access on September 28 and says the fee-recipient change was found and addressed the same day.
- check_circle The attacker diverted approximately 0.385 ETH in execution-layer staking rewards from certain validators.
- check_circle MetaMask reports no evidence that wallet infrastructure, withdrawal keys, Secret Recovery Phrases, private keys or staked principal were compromised.
- check_circle All affected validators were exited as a precaution, but an exit is distinct from the later withdrawal and possible reactivation of stake.
- check_circle Some staking customers experienced temporary withdrawal delays and may miss rewards while validators are exiting or awaiting reactivation.
- check_circle MetaMask says ordinary wallet users need take no action; affected staking customers should follow instructions delivered by MetaMask or their provider.
The Incident Reached A Reward Configuration Boundary
MetaMask says it identified unauthorized access to part of its infrastructure on September 28. Its September 30 notice described an ongoing response and the precautionary exit of affected validators in coordination with customers and partners. The November 5 update adds the material impact: an attacker briefly altered addresses used to receive execution-layer rewards for certain validators, and approximately 0.385 ETH was diverted before the issue was identified and corrected that day.
The company says all affected validators have now exited without incident. It reports no indication that MetaMask wallets or wallet infrastructure were compromised and no evidence that the event enabled access to or withdrawal of staked principal. It specifically says customer Secret Recovery Phrases, private keys and the withdrawal keys protecting staked ETH were not compromised. These statements define a narrower affected boundary than a general wallet breach.
MetaMask has not published the number of affected validators, the duration of the fee-recipient changes, the initial access method or the infrastructure component that stored the addresses. It also has not said whether 0.385 ETH represents the complete gross diversion before reimbursement or another accounting boundary. The confirmed incident should therefore be described as unauthorized infrastructure access with a brief fee-recipient alteration, not as theft of customer stake or compromise of the MetaMask extension.
Fee Recipients And Withdrawal Credentials Control Different Value
An Ethereum validator can earn value on two paths. Consensus-layer rewards update the validator balance for attestations and proposals. Execution-layer rewards, including transaction priority fees and some MEV-related value, are sent to a fee-recipient address configured by the validator operator. Ethereum's validator checklist treats that fee recipient as a setting supplied to the consensus client. Changing it can redirect execution rewards from future proposed blocks, but it does not rewrite the withdrawal credential recorded for the validator.
Withdrawal credentials determine where a validator's staked ETH and eligible balance are withdrawn. Ethereum documents 0x01 execution-address credentials and 0x02 compounding credentials as the authority for withdrawals and, after Pectra, certain execution-triggered actions. The withdrawal address is intended to remain under the stake owner's control and can be structurally separate from the hot validator key used for routine duties. That separation limited the consequence described by MetaMask.
MetaMask's own validator-staking documentation adds a service-specific layer. It says each validator uses a unique withdrawal smart contract that deducts the provider fee and directs the remainder to the depositing account, while MetaMask operates the validator infrastructure. The incident report says the attacker changed centrally stored fee-recipient addresses, not those withdrawal contracts or the customer's wallet keys. Responders should preserve that distinction because a visible unauthorized address in block rewards is serious evidence but is not proof that the principal withdrawal destination changed.
Exiting Validators Reduced Exposure Without Moving Funds Instantly
A validator exit stops future validation duties after Ethereum processes the request through its exit queue. It is not an immediate transfer of the validator balance. Once the validator becomes withdrawable, the protocol or service still has to process the withdrawal or sweep according to the credential type and service design. MetaMask warns that even after an exit, additional time may pass before funds can be withdrawn or staked again.
That timing explains two customer effects reported by MetaMask. Some affected staking customers experienced temporary withdrawal delays, and validators may miss rewards while exiting or waiting to be reactivated. Those availability and opportunity costs are different from unauthorized principal withdrawal. Provider dashboards may also show transitional states after the security issue itself has been contained.
Customers should not try to accelerate the process through links or transactions supplied by unsolicited support accounts. Use the normal MetaMask Portfolio route or the direct instructions from the contracted staking provider, verify the validator identifier and depositing account, and confirm each transaction in the wallet before signing. MetaMask says ordinary wallet users need take no incident-specific action and will never ask for a Secret Recovery Phrase or private key.
Onchain Verification Should Follow Each Validator
Affected organizations should record the provider notice, validator public keys or indexes, depositing account, expected withdrawal contract, historical fee recipient, exit state and every relevant timestamp. Preserve dashboard exports and support correspondence, but rely on onchain history for recipient changes and validator state where the protocol exposes them. Compare the fee recipient used for proposed blocks before, during and after September 28 with the provider's expected configuration.
Do not infer principal movement from a changed fee recipient. Verify consensus withdrawals and the withdrawal credential separately. Check the depositing account for expected claims, the unique withdrawal contract for its configured beneficiary, and the validator for exit and withdrawable state. If a partner manages part of the service, ask which party controlled validator signing, recipient configuration, withdrawal contracts and exit submission during the event.
Document missing rewards, delay and any provider reimbursement as separate accounting items. Preserve unfamiliar recipient addresses and transaction hashes without contacting them or sending test funds. MetaMask says it is working directly with affected customers and partners, so organizations that received no notice should avoid claiming exposure solely because they use the wallet. Their useful action is to review the service boundary and watch official updates.
Validator Operations Need Three Independent Control Planes
Validator operators should isolate at least three authorities: the hot signing key that performs validator duties, the configuration that selects an execution-layer fee recipient, and the withdrawal authority that controls principal and consensus withdrawals. A compromise of one plane should not silently grant the other two. Store withdrawal authority offline or behind a purpose-built contract, keep fee-recipient changes in a narrow service, and deny the ordinary validator runtime access to customer wallet secrets.
Fee-recipient changes deserve the same change-management quality as payment routing. Bind every update to a named validator set, require an approved destination, log the old and new address, and monitor proposed blocks for deviations. A second control can compare the runtime value with a separately maintained allowlist before a validator starts. Alert on drift immediately, because a rarely selected block proposer can hide a wrong recipient until a valuable proposal occurs.
Practice the exit path before an incident. Know who can submit exits, which validators can be handled in a batch, how queues and sweeps affect timing, how customers receive status, and what evidence proves that principal remains bound to the intended withdrawal credential. An emergency exit protects future operation only if teams can distinguish normal queue delay from a blocked or misdirected withdrawal.
Important Root Cause And Scope Questions Are Unanswered
MetaMask has disclosed the affected value path and the principal-protection boundary, but not the root cause. The public update does not identify the compromised service, credential or vulnerability; the number and ownership of validators; the exact recipient-change interval; the attacker; or whether a third-party operator first detected the change. It also does not publish indicators beyond the onchain behavior described in general terms.
The company says the unauthorized access is contained, affected systems are secured and all affected validators have exited. It reports no evidence of wallet or withdrawal-key compromise. Those are the current vendor findings, not a reason to widen the event into a general wallet alarm or to dismiss the confirmed reward diversion. A later technical report may change the number of affected systems, compensation detail or infrastructure controls without changing the protocol distinction between reward routing and withdrawal authority.
The practical lesson is not that self-custody removes infrastructure risk. MetaMask customers retained control of the withdrawal authority protecting principal, while a centrally operated configuration still controlled where some live rewards went. Secure staking services must expose both facts: which authority the user holds, and which value-moving settings the operator can change. Clear separation limits loss; clear monitoring and incident reporting make that limit verifiable.
Checklist
- Preserve the MetaMask or provider notice, validator identifiers, account addresses, timestamps and support correspondence.
- Verify historical execution-layer fee recipients and record every unauthorized address and affected block.
- Check the withdrawal credential, withdrawal contract beneficiary and principal movements separately from reward routing.
- Confirm each validator's exit, withdrawable and withdrawal state through provider and onchain evidence.
- Record diverted or missed rewards, queue delay and reimbursement as separate accounting items.
- Follow only direct provider instructions and never disclose a Secret Recovery Phrase, private key or withdrawal key.
- Track MetaMask updates for root cause, affected-validator count, access duration, indicators and compensation detail.
Sources
- MetaMask incident update: infrastructure access, reward diversion, validator exits and wallet boundary open_in_new
- MetaMask staking custody model: validator deposits, provider operation and user control open_in_new
- MetaMask validator staking: withdrawal smart contract, depositing account and operating model open_in_new
- MetaMask validator rewards: consensus rewards, block rewards, MEV and reward accounting open_in_new
- MetaMask staking timing: activation, exit and sweep queues open_in_new
- Ethereum.org withdrawal credentials: principal authority and withdrawal types open_in_new
- Ethereum Staking Launchpad: distinction between withdrawal credentials and fee recipients open_in_new
Continue Reading
OpenAM 16.1.4 Makes Session And Federation Trust Explicit
OpenAM 16.1.4 fixes live-session disclosure and unsigned SAML paths to account takeover. Upgrade, invalidate sessions and test federation policy.
Chainalysis Breach Makes Token Invalidation The First Recovery Boundary
Chainalysis says all users' password hashes and live tokens were exposed. Invalidate sessions, rotate API keys and verify every reconnect.
Botpress Incident Turns Bot Configuration Into A Credential Boundary
Botpress says forged staff sessions exposed integration credentials in 16 workspaces. Rotate provider-side secrets and reduce standing bot access.