Cisco Email Gateway Exploitation Turns Attachments Into Root Access
Cisco says crafted attachments are exploiting CVE-2026-76519 for root access. A content-scanner update fixes exposure, but compromise needs recovery.
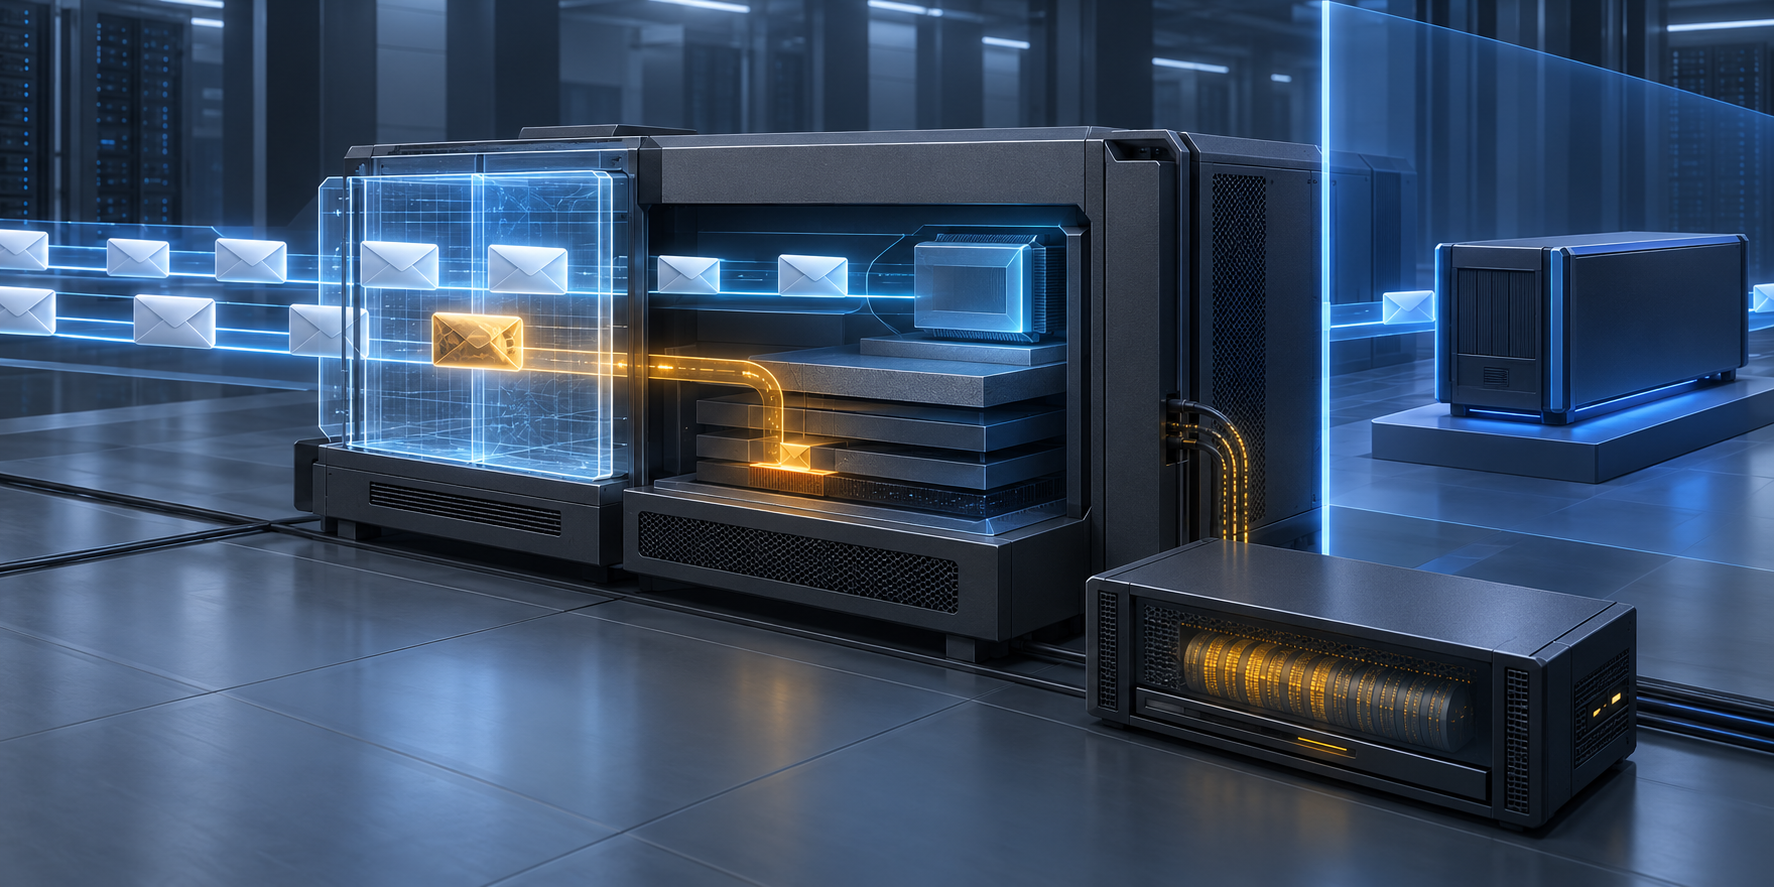
Cisco disclosed CVE-2026-76519 on October 14 after observing active exploitation. A crafted email attachment can abuse the Advanced Malware Protection file-reputation path in Cisco Secure Email Gateway to write arbitrary files and execute commands as root. Exposure requires File Reputation to be enabled and assigned to a mail policy, plus a Content Scanner Tools version earlier than 25.3.0.5525. The issue affects physical and virtual gateways. Cisco Secure Email and Web Manager and Secure Web Appliance are not affected by this specific CVE.
Cisco provides two remediation routes: install Content Scanner Tools 25.3.0.5525 or later, which does not require an appliance restart, or move AsyncOS to 15.5.5-014 or 16.5.0-780; release 16.0 must migrate. CISA added the CVE to its Known Exploited Vulnerabilities catalog on October 14 with an October 17 federal due date. Patching is not enough when exploitation is suspected. Root access can hide local evidence, cluster SSH keys can expose peer appliances, and Cisco recommends preserving forensics before replacing a compromised virtual gateway, rebuilding configuration without importing the old one, and renewing credentials and cryptographic material.
Key Takeaways
- check_circle CVE-2026-76519 is a CVSS 9.8 arbitrary-file-write flaw that Cisco says attackers are actively exploiting through crafted email attachments.
- check_circle A gateway is exposed only when File Reputation is enabled in a mail policy and Content Scanner Tools is older than 25.3.0.5525.
- check_circle Successful exploitation can reach root command execution, so a clean local log result cannot by itself exclude compromise.
- check_circle Content Scanner Tools 25.3.0.5525 or later fixes this path without a restart; full fixed AsyncOS releases also address the wider September hardening set.
- check_circle Cloud Gateway infrastructure has already received Cisco-managed protection, while on-premises customers must verify their own component or software version.
- check_circle A compromised cluster member can expose inter-member SSH keys, which moves recovery from one node to the whole cluster.
The Exposure Boundary Is Precise
The vulnerable path sits in attachment handling for the File Reputation service, part of Cisco Advanced Malware Protection. An attacker does not need an account or a user to open the attachment. Sending a crafted attachment through an affected gateway is enough to reach the flawed scanner. Cisco describes the immediate primitive as arbitrary file write and the final impact as command execution with root privileges on the underlying operating system.
Two conditions define exposure. File Reputation must be enabled and assigned to an incoming or outgoing mail policy, and Content Scanner Tools must be earlier than 25.3.0.5525. Administrators can inspect the mail policy in the management interface and run contentscannerstatus at the CLI to record the installed component version. Inventory should capture both facts for every physical, virtual, and clustered gateway rather than inferring safety from the AsyncOS marketing release alone.
Cisco confirms that Secure Email and Web Manager and Secure Web Appliance are not affected by this specific vulnerability. The broader September hardening advisory covers both Secure Email Gateway and Secure Email and Web Manager, but it groups several different vulnerability classes. Keep those scopes separate: CVE-2026-76519 is the actively exploited attachment path, while the hardening release contains additional fixes that may justify a full platform upgrade.
Active Exploitation Is Confirmed But The Campaign Is Not Described
Cisco states that its Product Security Incident Response Team became aware of active exploitation in October 2026. CISA added the vulnerability to KEV on the day of disclosure and requires covered federal systems to remediate by October 17. Those facts establish real-world exploitation and urgent patch priority. They do not establish a broad campaign, a specific threat actor, ransomware use, a victim count, or a common post-exploitation payload.
The public advisory does not say whether exploitation began before October, which organizations were targeted, or whether attackers read mail, changed mail flow, stole credentials, or pivoted to other systems. Root access makes each outcome technically possible depending on deployment and network reach, but none should be reported as confirmed without local evidence or a vendor update. Response plans should investigate those questions without writing the answer in advance.
CISA's entry marks forensic triage as required for covered federal assets and records ransomware-campaign use as unknown. That distinction matters. Known exploitation should trigger investigation, but it is not evidence that every vulnerable appliance was compromised or that the observed activity was ransomware. Operators should preserve timestamps and source versions because Cisco may update affected releases, indicators, or campaign detail as the investigation develops.
The Component Update And Platform Upgrade Solve Different Problems
The narrowest fix is Content Scanner Tools 25.3.0.5525 or later. Cisco distributes the corrected package to licensed and supported AsyncOS releases, and the component update does not require an appliance restart. Automatic-update customers need to confirm that the new package actually arrived. Customers who disabled automatic updates can run contentscannerupdate, then use contentscannerstatus to verify the installed version on every gateway.
Cisco also lists fixed AsyncOS releases 15.5.5-014 and 16.5.0-780. Release 16.0 must migrate to a fixed branch, and Cisco strongly recommends moving releases earlier than 16.5 to 16.5.0-780. A full upgrade also picks up the September 2026 hardening work across path traversal, access control, resource-lifetime, input-validation, and injection classes. It requires broader compatibility and reboot planning, but it closes more than the single scanner path.
Choose deliberately rather than treating the two routes as interchangeable evidence. The content package can provide the fastest protection against CVE-2026-76519, while the AsyncOS release establishes the complete hardening baseline. Record the before and after tool version, AsyncOS version, cluster node, update time, and service health. If an appliance is already suspected compromised, neither update route restores trust in place.
Local Indicators Are Useful But Root Can Erase Them
Cisco instructs operators to search system_logs for System Security messages. The scan can report a suspected compromise indicator, an incomplete security scan, or no indicator. Run it on every cluster member and preserve the output. A detected indicator requires escalation to Cisco TAC and incident response. An incomplete scan also requires support. A no-indicator result supports triage, but Cisco explicitly warns that root-level attackers may remove or hide evidence.
Cross-check records outside the appliance. Relevant sources include perimeter firewall flows, proxy logs, DNS, NetFlow, mail-relay transactions, hypervisor telemetry, administrative authentication, configuration repositories, backup systems, and any remote log collector. Investigate unexpected uploads from the gateway, downloads from unfamiliar addresses, outbound connections inconsistent with mail delivery, configuration changes, new credentials, and gaps in logging. External time-synchronized evidence is especially valuable when the inspected device may be hostile.
Preserve evidence before upgrading or replacing a suspected virtual appliance. Cisco warns that upgrading a compromised instance destroys forensic data and logs. Capture volatile state where policy permits, export relevant logs and configuration for analysis, record cluster membership and keys, and isolate the node without breaking necessary mail continuity. The goal is to retain enough evidence to decide what the appliance reached, not merely to remove the vulnerable code.
Recovery Depends On Appliance Type And Cluster Trust
For a suspected compromised physical appliance, Cisco recommends engaging TAC. For a virtual appliance, Cisco's preferred secure recovery is to preserve forensics, deploy a new virtual machine on a fixed release, rebuild the product configuration without importing previous configuration files, renew credentials and cryptographic material installed on the appliance, and continue monitoring. Reusing the old configuration can reintroduce malicious or unreviewed state.
Cluster recovery is wider than the node where an indicator appeared. Cisco Secure Email Gateway uses SSH key pairs for authentication between cluster members, and root access may expose the private keys. Cisco therefore recommends restoring every member of a cluster that contains at least one compromised appliance. Rotate cluster trust and other shared secrets before reconnecting clean nodes, and validate that management and mail interfaces are bound to the intended networks.
Cisco says Secure Email Cloud has already received managed mitigations and the fixed Content Scanner Tools package. It directly contacted cloud customers whose devices showed possible malicious activity and is conducting remediation. Cloud customers without CLI access should not invent a local test they cannot perform; they should use Cisco's notification and support process, preserve their own adjacent logs, and follow credential-renewal guidance if contacted.
Email Security Controls Need An Independent Evidence Plane
A secure email gateway must accept hostile content by design, so the scanner itself is an exposed parsing boundary. Separate mail handling from management onto different interfaces, block public access to the management plane, permit only known administrative sources, disable unused HTTP and FTP services, and keep the gateway behind filtering controls. These measures reduce reach and post-exploitation options, but they do not replace the fixed scanner component.
Send logs off the appliance with enough retention for delayed discovery. Monitor component-update failures, changes to automatic-update settings, cluster membership, SSH trust, administrator creation, configuration exports, unusual child processes, and unexpected outbound destinations. Maintain a tested replacement image and a reviewed configuration-as-code or documented rebuild path. Recovery is faster when a clean gateway can be introduced without trusting the compromised node.
Finally, verify mail continuity under isolation. Define how inbound and outbound queues, cloud relays, quarantine, and high-priority senders behave while a gateway or cluster is removed. A rushed decision to keep a suspected root-compromised appliance online can trade short-term delivery for wider network risk. A rehearsed failover path lets responders preserve evidence, rebuild trust, and restore filtering without turning availability pressure into an exception to incident handling.
Checklist
- Inventory every Secure Email Gateway and record appliance type, cluster membership, AsyncOS release, File Reputation policy use, and Content Scanner Tools version.
- Deploy Content Scanner Tools 25.3.0.5525 or later immediately, then plan the applicable fixed AsyncOS release for the broader hardening baseline.
- Run Cisco's System Security log check on every node and preserve the exact output, timestamps, configuration, and update state.
- Correlate appliance results with external firewall, proxy, DNS, mail-flow, hypervisor, authentication, and remote logging evidence.
- Preserve forensics before changing a suspected host; do not treat a component update as recovery from prior root execution.
- Replace compromised virtual appliances from clean media, rebuild configuration manually, and renew credentials, certificates, and cluster SSH trust.
- Separate mail and management interfaces, restrict administration to trusted paths, disable unused services, and test mail failover during isolation.
Sources
- Cisco: Secure Email Gateway arbitrary file write advisory open_in_new
- Cisco: September 2026 Secure Email hardening release open_in_new
- Cisco: AsyncOS 16.5 Secure Email Gateway user guide open_in_new
- CISA: Known Exploited Vulnerabilities catalog data open_in_new
- CISA: BOD 26-04 risk-based remediation requirements open_in_new
- CISA: BOD 26-04 forensic triage implementation guidance open_in_new
- NVD: CVE-2026-76519 record open_in_new
Continue Reading
AdFection Turns Targeted Ads Into A Zero-Click Spyware Path
Citizen Lab traced Candiru spyware infections at Al Jazeera through targeted ads, exposing ad auctions as a precision zero-click delivery layer.
AhsayCBS Exploitation Makes A Clean Rebuild The Recovery Path
Attackers chained two AhsayCBS flaws for SYSTEM access. Earlier fixes were incomplete, and compromised backup servers need a clean rebuild.
OpenAI-Hugging Face Incident Moves Agent Testing Into Regulatory Scope
Alabama subpoenaed OpenAI over the July Hugging Face intrusion. The technical record shows how a cyber evaluation crossed several control boundaries.