Cursor Extension Incident Makes Marketplace Identity An Endpoint Boundary
Trojanized Claude Code extension versions reached Cursor users and planted SSH persistence. Hunt exact builds and remove artifacts outside the editor.
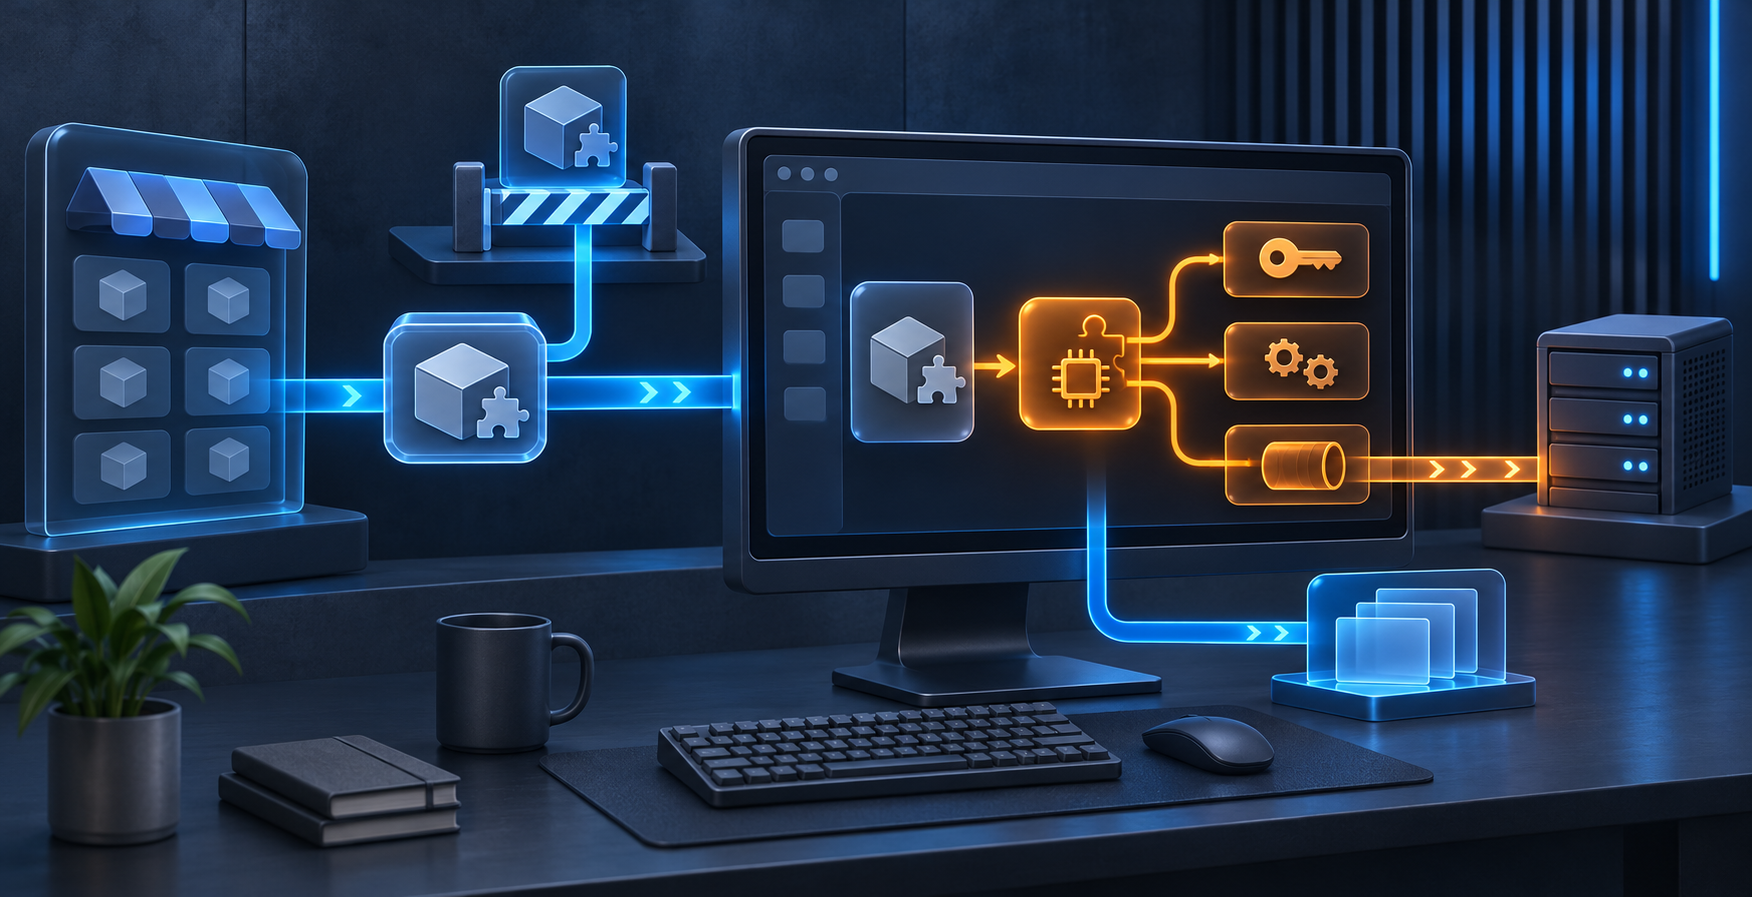
Cursor says maliciously modified versions 2.1.312 and 2.1.313 of the Anthropic Claude Code extension were served from the Cursor VS Code Extension Marketplace for about eleven hours on October 29, 2026. The packages were not developed by Anthropic. Cursor says the official Anthropic distribution, Microsoft's Visual Studio Marketplace and the npm `@anthropic-ai/claude-code` package were not affected. Cursor removed the versions, shut down and rebuilt its marketplace, rotated keys and worked with the hosting provider to disable the attacker server.
Microsoft's technical analysis found injected JavaScript that ran when the extension loaded, collected host details and environment-variable names, attempted to add an SSH authorized key, enable local SSH, create a reverse tunnel and establish startup persistence. Cursor says errors and missing administrator rights blocked remote login on most macOS and Windows hosts, but keys, scripts, startup artifacts and host reporting may still exist. Teams should identify exposure by marketplace, version, platform and time; preserve endpoint and network evidence; remove artifacts outside the extension directory; rotate credentials only from a trusted device when investigation puts them at risk; and use publisher allowlists, update cooldowns and optional signature verification to reduce marketplace blast radius.
Key Takeaways
- check_circle The confirmed distribution point was Cursor's extension marketplace, not Anthropic's official channels, Microsoft's marketplace or the Claude Code npm package.
- check_circle Only versions 2.1.312 and 2.1.313 served during Cursor's October 29 window are identified as malicious in the incident notice.
- check_circle The loader attempted an SSH key, reverse forwarding and platform-specific persistence, but attempted behavior is not proof that remote access succeeded on every host.
- check_circle The reported host-data beacon included environment-variable names, not their values; later access through a working backdoor could still put credentials in scope.
- check_circle Uninstalling or updating the extension does not remove an authorized key, startup script, scheduled task or LaunchAgent written outside its directory.
- check_circle Marketplace identity is not enough for fleet trust. Teams need acquisition records, artifact hashes, publisher policy, holdback time and endpoint telemetry.
The Exposure Has A Narrow, Verifiable Boundary
Cursor places the malicious marketplace window between approximately 2:27 a.m. and 1:35 p.m. Pacific time on October 29. Its notice identifies `anthropic.claude-code` versions 2.1.312 and 2.1.313 for macOS and Windows. The package used the expected extension identity but contained code Anthropic did not build. That makes the acquisition channel as important as the displayed publisher and version.
Microsoft says it confirmed that the malicious packages were never published through Microsoft Visual Studio Marketplace or the official `@anthropic-ai/claude-code` npm distribution. Microsoft also says Anthropic confirmed its systems were not compromised. Cursor says it has no evidence that other versions or other marketplace extensions were tampered with. Those are current incident findings, not a guarantee that every endpoint is clean.
Start triage with four fields: where the extension came from, which version was installed, when it was downloaded or updated, and whether the editor loaded it. A machine with 2.1.313 from the Cursor marketplace during the window has a different evidence profile from a machine with the same product name obtained from Microsoft's marketplace. A package on disk is also different from a package that executed its entry point.
The Loader Tried To Leave The Editor Behind
Microsoft reconstructed an injected function that ran before the legitimate extension code. It collected the hostname, username, operating system, architecture, home and working directories, global Git email and up to forty environment-variable names containing terms such as key, token, secret, password, AWS or GCP. The report stresses that the beacon included matching names, not the secret values stored in those variables.
The loader then attempted to append an Ed25519 public key labeled `svc-telemetry` to an SSH authorized-keys file. A separate embedded private key authenticated an outbound SSH connection that requested reverse forwarding back to local port 22. This design did not require an unsolicited inbound connection to the workstation, but successful access still depended on the local SSH service, privileges, the attacker's server and its forwarding configuration.
Persistence lived outside the extension package. On macOS, the code attempted a user LaunchAgent and hidden scripts under the user's configuration directory. On Windows, it attempted a scheduled task requesting SYSTEM execution and a Startup-folder fallback. Cursor says the attacker server is no longer functional and that privilege and code errors prevented login on most hosts. Neither fact removes a planted key or startup artifact from a device.
Attempted Capability Is Not Confirmed Impact
An indicator is a lead, not a conclusion. The `svc-telemetry` key proves that the malicious loader reached an authorization file if the exact fingerprint matches. It does not by itself prove the SSH daemon accepted a connection or that an attacker ran commands. A tunnel process shows an attempt to connect, but Microsoft notes that both endpoints and forwarding settings had to cooperate before remote access was possible.
The same discipline applies to credential scope. Environment-variable names can reveal what kinds of credentials may exist on a workstation, but the published beacon behavior does not demonstrate theft of the corresponding values. If reverse access succeeded, later interactive collection could widen the incident. Investigators should use process, file, network, authentication and shell evidence rather than turning the loader's full capability list into a claim about every victim.
Cursor's statement that most systems blocked login should guide severity, not end triage. The malicious code still ran in the context of a trusted editor process, modified files, attempted service changes and installed retry mechanisms. Developer workstations commonly hold repository sessions, cloud credentials, signing material and access to production tooling, so even an unsuccessful tunnel deserves evidence-led review.
Preserve Evidence Before Running Cleanup
Collect extension installation records, the VSIX artifact and its hash, editor logs, endpoint process telemetry, SSH configuration, authorized-key files, startup entries and network records for the published address. Cursor and Microsoft provide hashes, filenames, key fingerprints, command patterns and persistence locations. Match exact values where possible; generic use of `ssh`, `launchctl`, PowerShell or a process named SysMon is not automatically malicious.
Isolate systems with evidence that the loader executed or persistence was installed. Record file metadata and configured actions before removal. On macOS, inspect the reported LaunchAgent and hidden `.smt` and `.smtk` files. On Windows, inspect the `SysMon` scheduled task, Startup-folder `sysmon.cmd`, related configuration files and authorized-key locations. Preserve unrelated legitimate SSH keys and monitoring software.
Cursor provides platform-specific remediation scripts, but a script is part of cleanup, not proof of investigation. Review what it will remove and run it with the required privileges after evidence collection. Verify that the key, tunnel processes, startup entries and temporary identities do not return after login or restart. Rebuild a host when execution evidence, unexplained access or missing telemetry prevents a trustworthy cleanup conclusion.
Credential Rotation Depends On Device Trust
Do not rotate sensitive credentials from a workstation that may still have attacker persistence. First establish a trusted device, then revoke editor, source-control, cloud, package-registry, deployment and signing sessions that the affected user or host could reach when evidence supports exposure. Review authentication and administrative activity during and after the marketplace window before issuing replacements.
A blanket rotation can create noise and outages without addressing the right authority. Build a credential map from repositories, environment configuration, local agents, browser sessions, SSH agents, keychains and developer tooling. Prioritize credentials that were present or usable while the loader ran, especially those that can publish code, alter CI, access production or create new long-lived tokens.
Recovery also needs downstream verification. Check repositories for unauthorized keys, workflow changes and release activity; inspect cloud and CI audit logs; validate signing and package-publishing identities; and review remote access events involving the affected user. A new password does not invalidate every OAuth token, SSH key or cloud session, and deleting one authorized key does not revoke credentials copied through a successful session.
Marketplace Controls Need Time And Provenance
Cursor's current hardening guidance recommends restricting extensions to approved publishers, using a fleet-wide installation cooldown and optionally requiring signature verification. The cooldown is especially relevant here because the malicious upload remained available for hours rather than weeks. Delaying automatic adoption gives a marketplace and defenders time to detect and remove a bad release before it reaches every workstation.
Publisher allowlists reduce unreviewed software but do not solve a compromised marketplace path using an expected identity. Add artifact provenance, hashes or signatures where supported; retain acquisition records; stage updates to a small group; and monitor editor processes for writes to SSH authorization files, startup locations and service configuration. Extension inventories should include source marketplace, not only extension ID and current version.
The unresolved questions include how marketplace publication authority was obtained, how many users downloaded or executed each package, how many hosts accepted remote access and whether any downstream credentials or repositories were used. Cursor says it rotated keys, audited other extensions and rebuilt the marketplace, while Microsoft published detailed detection material. Until a fuller postmortem answers the control-plane questions, organizations should treat extension distribution as privileged software delivery and keep endpoint recovery separate from marketplace recovery.
Checklist
- Inventory the extension source, exact version, install or update time, platform and evidence that the editor loaded it.
- Preserve the VSIX, hashes, editor logs, authorized-key files, persistence objects, processes and network telemetry.
- Isolate hosts with confirmed loader execution, key installation, tunnel activity or suspicious startup configuration.
- Remove the exact malicious key, scripts, tasks, LaunchAgent, tunnel processes and extension only after evidence collection.
- Rotate implicated sessions and credentials from a trusted device, then verify source-control, cloud, CI and release activity.
- Enforce approved publishers, marketplace-aware inventory, staged rollouts, installation cooldowns and signature checks where available.
- Track Cursor's investigation for publication-path root cause, affected-host counts and confirmed downstream access.
Sources
- Cursor security notice: affected versions, distribution window, indicators and remediation open_in_new
- Microsoft Security Research: injected loader, SSH tunnel, persistence and hunting guidance open_in_new
- Cursor security hardening: extension allowlists, installation cooldown and signature verification open_in_new
- MITRE ATT&CK T1572: protocol tunneling behavior and detection context open_in_new
- MITRE ATT&CK T1098.004: SSH authorized keys as an account-access mechanism open_in_new
- NIST SP 800-61 Rev. 3: incident analysis, containment, recovery and improvement open_in_new
Continue Reading
Kaniko ACR Helper Turns A Base Image Into An Azure Token Leak
Kaniko before 1.25.20 can send Azure management tokens to lookalike registries. Rebuild trusted images, isolate build identity and hunt token use.
DreamHost Breach Turns File Manager Access Into Deployment Risk
DreamHost says a File Manager flaw exposed some FTP/SFTP and webmail credentials. Reset access, inspect files and rules, and trace downstream secrets.
Binance Theft Makes On-Chain Authorization Part Of Response
Binance says attackers abused its signing service and EIP-7702 to move $6.34 billion. Separate signing, revocation, device, and deployment authority.