DreamHost Breach Turns File Manager Access Into Deployment Risk
DreamHost says a File Manager flaw exposed some FTP/SFTP and webmail credentials. Reset access, inspect files and rules, and trace downstream secrets.
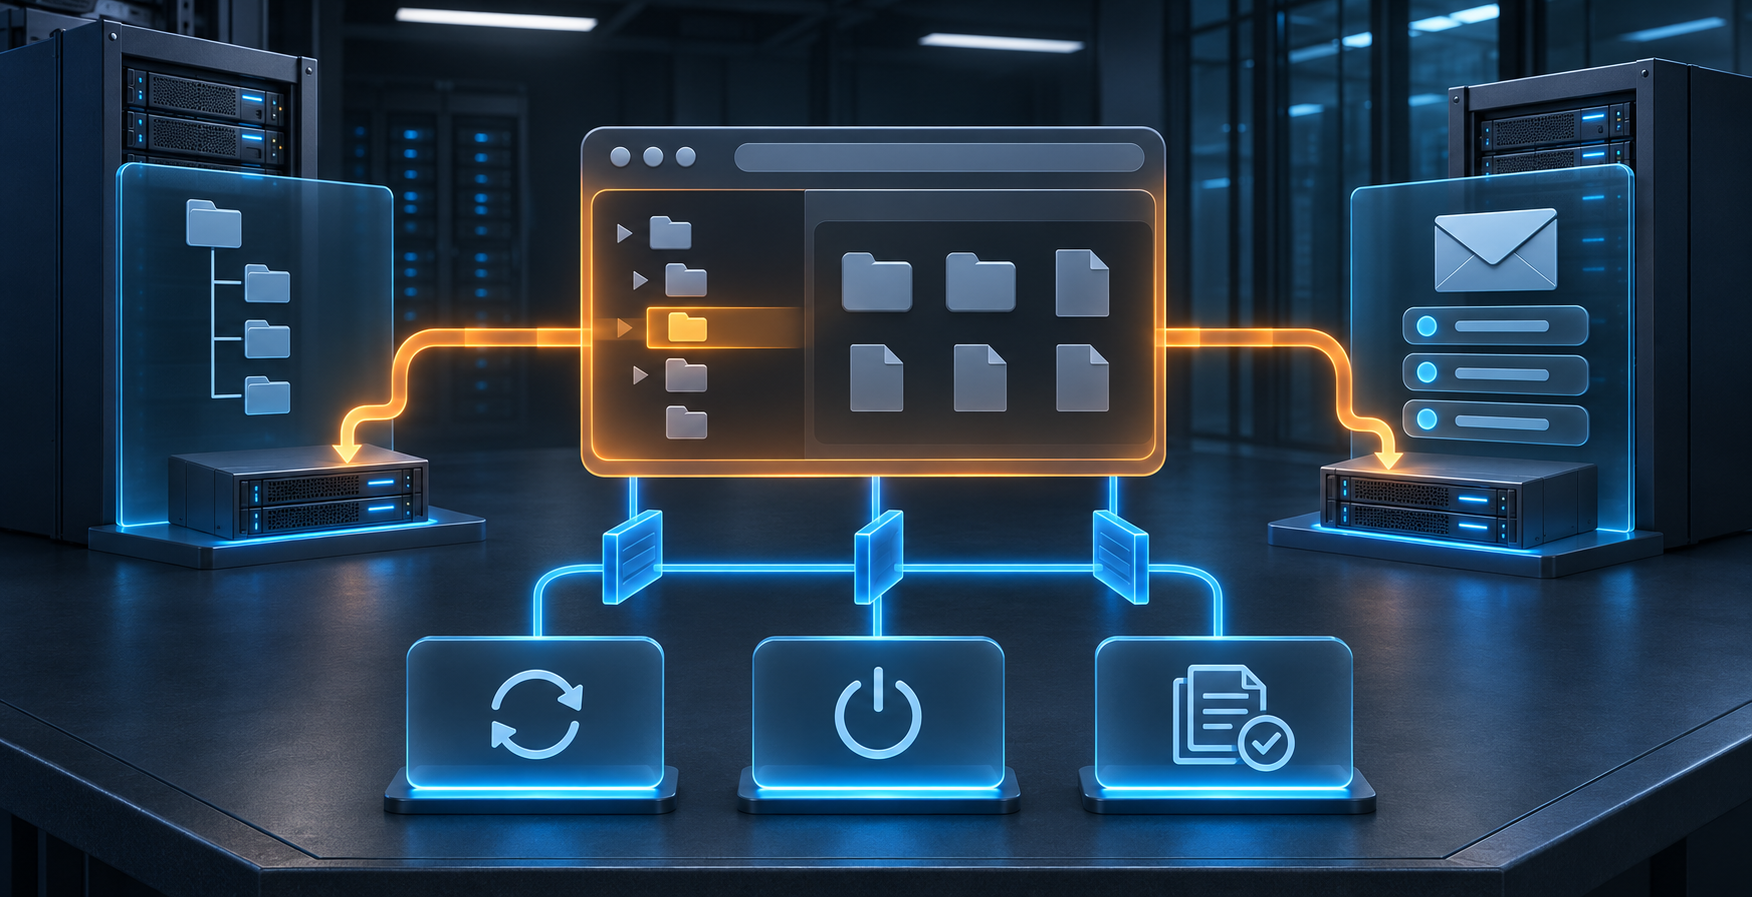
DreamHost says an unauthorized third party exploited a vulnerability in third-party software behind its browser-based File Manager. The attacker could obtain FTP/SFTP usernames and passwords for users who logged into the tool from approximately August through October 23, 2026, and could reach certain webmail systems. DreamHost says the incident affected well under 10 percent of hosted email and FTP/SFTP accounts, reset passwords for accounts it believed could be affected, terminated relevant sessions and rebuilt the File Manager environment.
The response cannot stop at changing one hosting password. Website credentials can modify executable content, steal configuration secrets or create persistence, while webmail access can expose messages, forwarding rules and recovery links. A formal notice filed with California says affected data may have included File Manager or webmail credentials, mailbox contents and files on FTP/SFTP servers. Account owners should preserve notices, inventory every affected user, compare website files with known-good releases, review mail rules and sessions, rotate downstream secrets found in accessible files or messages, and keep vendor-confirmed scope separate from possibilities still under investigation.
Key Takeaways
- check_circle DreamHost attributes the incident to a vulnerability in third-party software used by its browser-based File Manager.
- check_circle The stated exposure window covers users who logged into File Manager from approximately August through October 23, not every DreamHost customer or every hosted account.
- check_circle DreamHost says well under 10 percent of hosted email and FTP/SFTP accounts were affected and says it found no evidence of control-panel or billing-data access.
- check_circle The California notice says session credentials, mailbox contents and hosted files may have been accessed, which makes website and mail review as important as password reset.
- check_circle A changed SFTP password does not remove an altered site file, unauthorized mail rule or secret copied from configuration or email.
- check_circle The investigation is ongoing, and DreamHost has not publicly identified the third-party File Manager product, vulnerability identifier or total number of confirmed accounts.
What DreamHost And The Regulator Notice Confirm
DreamHost says it discovered unauthorized access to the server running `files.dreamhost.com` on October 23. The File Manager is a browser-based tool built on third-party software. According to the company, the attacker exploited a vulnerability in that software and could access FTP/SFTP usernames and passwords belonging to users who had logged into File Manager between approximately August and October 23. DreamHost took the File Manager offline, addressed the vulnerability and began a forensic investigation.
The company also says the attacker reached certain webmail systems and obtained login credentials for a limited number of users. DreamHost reset implicated passwords and terminated active sessions on October 23. Its public announcement says it believes mailbox contents may have been viewed in a small number of cases and that it is contacting those customers individually. The California filing records August 15 as a known breach date, while the sample notice describes the access and affected-login window more broadly as between August and October 23.
DreamHost estimates that the event affected a fraction of hosted email and FTP/SFTP accounts, well under approximately 10 percent. That is a proportion, not a published account count. The company says it has found no evidence that the attacker accessed DreamHost control-panel logins or customer billing details, and says full payment-card numbers are handled by a third-party processor. Those negative findings are important, but they do not narrow the confirmed website and mail exposure to zero.
The File Manager Became A Credential Broker
SFTP encrypts a connection in transit, but it cannot protect a password after that password is entered into a compromised application. The vulnerable File Manager sat between a user's browser and the hosted file service. That position let the incident cross a boundary that teams often miss: a convenience interface can become a credential broker for a more privileged deployment channel.
DreamHost's notice does not say that every login during the period was captured or successfully used. It tells potentially affected users to treat the relevant usernames and passwords as compromised. The distinction matters. Exposure of a credential is confirmed for the affected population, while attacker use, file modification and downstream access need account-specific evidence.
Account owners should build that evidence from panel records, user inventory, SFTP and shell logs where available, file modification times, deployment history, source-control state and application telemetry. A password reset closes future password use. It does not answer whether a valid login wrote a web shell, replaced a dependency, downloaded a backup, copied an environment file or modified a site before containment.
Website Access Expands Into Secret And Integrity Risk
A website user can hold more authority than its name suggests. Depending on directory ownership and application design, the account may reach source files, deployment artifacts, database configuration, API keys, mail credentials, backup archives and writable web roots. DreamHost's own security guidance recommends one user per domain so compromise of one site is less likely to expand into others. Owners should verify whether that separation actually existed for every affected username.
Start with integrity, not only availability. Compare deployed files against a known-good release or clean backup, review new and recently changed executable files, inspect scheduled jobs and startup hooks available to the account, and look for unexpected administrator accounts in the application itself. Preserve suspicious files and logs before deleting them. Rebuilding from reviewed source may be safer than trying to prove every file in a long-lived shared tree is clean.
Then identify secrets that were readable from the account. Rotate database passwords, API tokens, webhook URLs, signing keys and deployment credentials at their issuing systems when the evidence or access model puts them in scope. Updating a copied value inside one configuration file is not revocation. Verify every consumer after rotation, and separate credentials by site and environment so the next exposed file account does not become a portfolio-wide incident.
Webmail Exposure Is A Session And Recovery Problem
The formal notice says certain webmail systems may have exposed session information, including session credentials that keep a user signed in. DreamHost says it terminated active sessions for users who may have been affected. That is a separate control from resetting a password: a valid session can sometimes survive a password change unless the service explicitly revokes it.
Review mailbox forwarding rules, filters, delegates, recovery addresses and sent items for changes that do not belong. Search for messages containing password resets, cloud invitations, invoices, customer exports or configuration attachments that could create additional exposure. Do not assume the attacker read every mailbox. DreamHost describes mailbox-content access as a belief in a small number of cases, while the regulator notice says content may have been accessed for notified recipients.
Communicate new passwords to managed mail users through a channel other than the affected mailbox. DreamHost notes that only the account holder can set new mail and website-user passwords in the control panel. Users should type the panel address directly rather than follow password-reset links in email, because a real incident gives phishers a credible pretext and affected mail users may be waiting for access instructions.
Account Owners Need One Coordinated Response
Export or record the account's current mail, SFTP and shell users before making further changes. Match DreamHost notices and forced resets to individual users, domains, clients and devices. Replace stored passwords in mail clients, deployment jobs and SFTP tools only after the panel reset takes effect. Remove dormant users rather than assigning them another long-lived password.
Create one incident timeline that covers File Manager logins, password resets, session termination, website changes, mail-rule changes, secret rotation and customer notification decisions. If hosted files or mail contain personal information belonging to other people, the hosting customer may have separate contractual or legal duties. DreamHost explicitly tells such customers to consider those obligations; the vendor's own notice does not automatically complete a customer's assessment.
Keep the scope precise. Users who did not receive a notice are not told that action is required, although DreamHost allows precautionary changes. Users whose old password still works are described by the company as not exposed based on the investigation to date. Those statements can guide triage, but organizations with high-impact sites should still validate file integrity and account inventory because their risk depends on what each hosting user could reach.
The Root Cause And Final Scope Remain Open
DreamHost says it preserved the affected server, rebuilt File Manager with additional precautions, rotated potentially exposed internal credentials and retained outside forensic experts. It is also reviewing other customer-facing tools for similar flaws. Those are meaningful containment steps, but the company has not publicly named the third-party product, the vulnerable component version, a CVE or the exact control that allowed access to credentials.
The public records also leave several measurements unresolved: how many accounts were confirmed exposed, how many credentials were used, how many websites or mailboxes were accessed, and whether any persistent changes were found after password and session resets. The formal notice offers a wider possible-data statement than the shorter website announcement, so affected organizations should retain both documents and any individualized communication.
Close response only after the account-specific questions are answered. A vendor can fix the shared File Manager and revoke known sessions, but each customer owns the integrity of its deployed application, the secrets stored beside it and the recovery role of its mailbox. The durable lesson is that a browser convenience layer with access to deployment credentials belongs in the same threat model as the deployment plane itself.
Checklist
- Record every affected mail, SFTP and shell user, its domains, owners, clients and last known File Manager use.
- Reset implicated passwords only through the DreamHost control panel and remove dormant users instead of re-enabling them.
- Compare website files, jobs and application administrators against known-good source, backups and deployment records.
- Review webmail sessions, forwarding rules, filters, delegates, recovery settings and sensitive messages.
- Rotate readable database, API, webhook, signing and deployment secrets at their issuing systems, then verify consumers.
- Preserve notices, logs and suspicious artifacts in one timeline before cleanup or rebuild work removes evidence.
- Track DreamHost's investigation for a final account count, root cause, affected-data boundary and additional notifications.
Sources
- DreamHost incident announcement: attack path, affected services, scope and response open_in_new
- California Attorney General filing: submitted DreamHost breach notice and known breach date open_in_new
- DreamHost sample breach notice: possible credentials, sessions, mailbox and hosted-file access open_in_new
- DreamHost status timeline: File Manager outage, password resets and customer instructions open_in_new
- DreamHost website security guidance: isolated users, SFTP and file-permission boundaries open_in_new
- NIST SP 800-61 Rev. 3: evidence-led incident response and recovery planning open_in_new
Continue Reading
GitBook Incident Turns SSO And Integrations Into A Production Path
GitBook says an SSO flaw led from staff sessions to code, cloud keys and customer secrets. Rotate exposed trust and audit connected repositories.
Kaniko ACR Helper Turns A Base Image Into An Azure Token Leak
Kaniko before 1.25.20 can send Azure management tokens to lookalike registries. Rebuild trusted images, isolate build identity and hunt token use.
Cursor Extension Incident Makes Marketplace Identity An Endpoint Boundary
Trojanized Claude Code extension versions reached Cursor users and planted SSH persistence. Hunt exact builds and remove artifacts outside the editor.