Linux IPv4 Race Makes Kernel Patching A Network Perimeter Issue
CVE-2026-98432 reaches Linux kernel memory through IPv4 TCP handshakes. Track distro fixes, test packet filters, reboot, and prove the runtime.
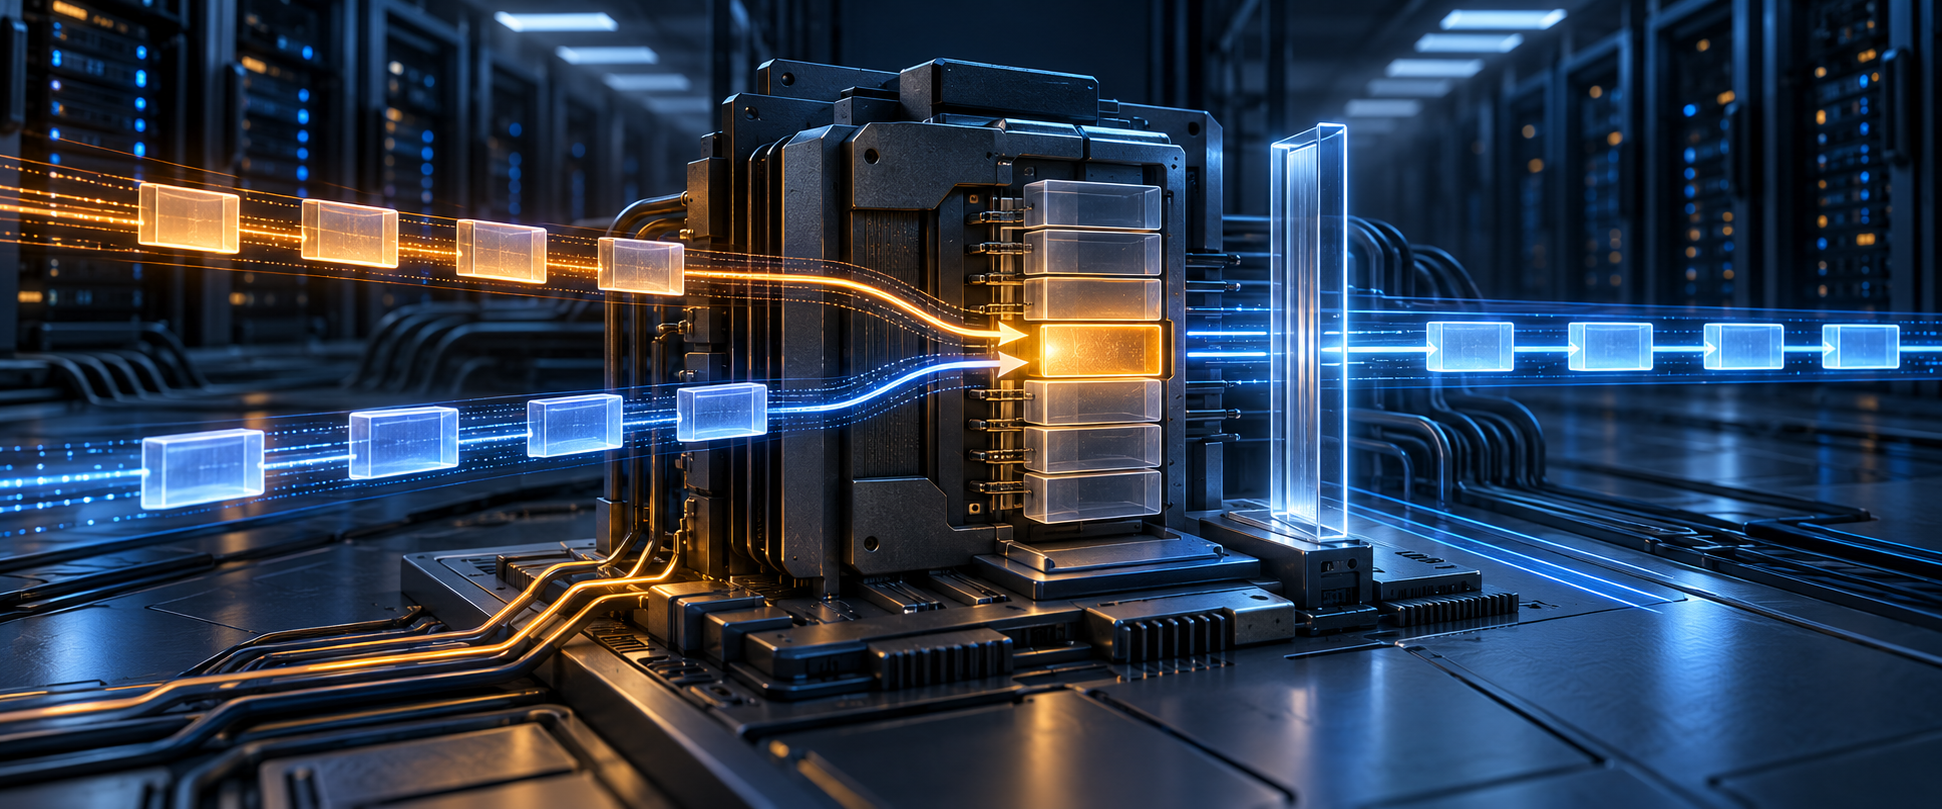
Red Hat issued a critical October 30 bulletin for CVE-2026-98432, a use-after-free race in the Linux IPv4 TCP connection path. A retransmitted SYN can leave one CPU building a SYN-ACK from socket options while another path frees the same memory. The upstream fix defers that free until an RCU grace period has passed. The vulnerable code runs before an application accepts the connection, so ordinary service hardening does not remove the kernel exposure.
Anthropic reports a working exploit against a Linux server with a Multipath TCP listener that leaks a kernel pointer and eventually runs an attacker-chosen command as root. That demonstrated chain is narrower than every IPv4 TCP listener, while the underlying crash and memory-corruption path is broader. Distribution fixes were still uneven on October 31: Red Hat was expediting updates, Ubuntu listed major kernel packages as vulnerable or work in progress, and AlmaLinux had patched builds in testing. Operators need vendor-specific tracking, temporary filtering where safe, a reboot into the fixed kernel, and runtime proof.
Key Takeaways
- check_circle CVE-2026-98432 is reachable through incoming IPv4 TCP connection requests carrying IP options; it does not require an authenticated application session.
- check_circle The race can produce a crash or memory corruption, and Anthropic reports a complete remote-root chain against a server with an MPTCP listener.
- check_circle The demonstrated MPTCP exploit does not prove that every ordinary TCP listener is immediately exploitable for code execution, but those systems still reach the vulnerable kernel path.
- check_circle The upstream correction replaces immediate frees with RCU-delayed frees, and maintained stable kernel branches have received backports.
- check_circle A fixed upstream branch does not mean a distribution package is available; vendor advisories and package status are the authoritative deployment boundary.
- check_circle Dropping inbound IPv4 TCP packets with IP options and disabling unused MPTCP can reduce exposure, but neither replaces a fixed kernel and a reboot.
What Changed On October 30
The Linux kernel CVE record appeared on October 15, but the operational picture sharpened at the end of the month. Anthropic published its working remote-root chain on October 27. Red Hat followed on October 30 with critical bulletin RHSB-2026-016, stating that unauthenticated network traffic can trigger memory corruption or a crash and that it was expediting fixed packages. Ubuntu updated its package matrix the same day, while AlmaLinux published testing builds for releases 8, 9, and 10.
The CVE and Red Hat currently use a 9.8 CVSS 3.1 vector with network access, low complexity, no privileges, and no user interaction. Ubuntu labels its operational priority High while displaying the same critical base score. Those labels are inputs to triage, not a substitute for reachability and package status.
None of the cited vendor records says the vulnerability is being maliciously exploited in the wild. Anthropic's result is a controlled proof that remote root execution is possible in a defined setup. Teams should prioritize exposed systems without turning a demonstrated exploit into an unsupported claim that all internet-facing Linux hosts have been compromised.
The Race Happens Before The Application
When an IPv4 TCP SYN carries IP options, the kernel saves those options on the pending request so it can use them while constructing a SYN-ACK. During connection creation, the option pointer is transferred to the child socket rather than copied. A second CPU can process a retransmitted SYN and keep reading the request options while the newly created child socket is destroyed and frees that same memory.
The readers already operate under read-copy-update protection, but the two destructor paths used an immediate `kfree()`. The upstream patch changes them to `kfree_rcu()`, delaying reclamation until pre-existing readers have left their critical sections. It also addresses a related request-socket migration path. The main IPv6 connection path is not affected because it copies the options; the upstream record notes a narrower IPv6 migration case involving CALIPSO for separate work.
Because the kernel processes the crafted handshake before a web server, SSH daemon, reverse proxy, or containerized application accepts it, application authentication and request validation never see the trigger. Network address translation and load balancers may change reachability, but they should be tested rather than assumed to remove crafted IP options. The host kernel remains the enforcement point for traffic delivered to local services and many container workloads.
What The Working Exploit Proves And What It Does Not
Anthropic says its exploit targets a server with a Multipath TCP listener. It first wins the race to make the kernel return excess memory, repeating until a reply contains a kernel pointer and defeats address randomization. It then uses the same use-after-free to corrupt memory, redirect a callback, and run a shell command as root. The reported laboratory timing was about 48 minutes for the address leak and another five minutes for command execution.
That is a vendor research claim backed by coordinated disclosure and an upstream fix. It establishes that the bug can cross the boundary from denial of service into control of the kernel under the tested conditions. It does not establish a five-minute universal exploit, nor does it show the same chain against every distribution, architecture, kernel configuration, or regular single-path TCP service.
MPTCP is therefore an important exposure multiplier, not the definition of the vulnerability. AlmaLinux says MPTCP is disabled by default on its systems, while the regular IPv4 TCP bug remains present and still requires patching. Inventory `net.mptcp.enabled`, active MPTCP listeners, BPF request-migration use, internet-facing TCP listeners, and hosts reachable from guest, tenant, or partner networks.
Patch Availability Is A Distribution Question
Anthropic says the correction was patched upstream and backported to all maintained stable kernel branches. That statement describes source trees. Production systems normally consume kernels from a Linux distribution, cloud image, appliance vendor, or managed platform that applies its own backport, builds packages, tests them, and publishes an advisory.
As of the dated sources, Red Hat lists RHEL 8, 9, 10, RHEL CoreOS, and dependent OpenShift environments as affected and says fixes are being expedited. Ubuntu's October 30 matrix marks the main 26.10, 26.04 LTS, 24.04 LTS, and 22.04 LTS kernel packages as vulnerable with work in progress, with other flavors tracked separately. AlmaLinux offers patched 4.18, 5.14, and 6.12 builds in its testing repository, not yet its production repositories.
Do not compare only the visible upstream version number. Enterprise distributions routinely backport security changes without rebasing to a new mainline release. Match each running package to its vendor CVE page or security notice, include cloud and real-time variants, and treat immutable nodes as image-replacement work. Containers share the host kernel, so rebuilding an application image does not remediate the node.
Use Temporary Controls With Their Failure Modes Visible
Red Hat recommends a temporary nftables rule that drops incoming IPv4 TCP packets whose IPv4 header contains options. Standard TCP options such as window scaling and timestamps live in the TCP header and are not removed by that rule. Test the filter against real traffic, routing, encapsulation, and failover before deployment, then confirm counters and service health.
The control is not universal. AlmaLinux warns that routed traffic may also be dropped, same-host container traffic may bypass the chosen hook, and environments using CIPSO or NetLabel security labels rely on IPv4 options. A filter at a cloud edge or appliance may normalize or discard options, but prove its behavior with a safe test rather than inferring it from a product category.
If MPTCP is enabled and not required, disable it and restart services that already own MPTCP listeners. That removes the setup used in Anthropic's demonstrated chain, but it does not close the regular IPv4 race. Keep the packet filter and MPTCP change documented as temporary exceptions, with an owner and removal condition after a supported kernel is installed.
Reboot, Prove The Runtime, And Preserve Kernel Evidence
Installing a kernel package is only half the change. Schedule the reboot or node replacement required to load it, then record the running kernel with `uname -r` and compare that exact build with the vendor's fixed package. In clusters, verify every node and prevent vulnerable nodes from rejoining through an old autoscaling image or rollback pool.
The vulnerable work occurs before application logs receive a connection. Preserve firewall and flow records, load-balancer telemetry, packet captures where policy allows, kernel journals, crash dumps, console logs, reboot history, and cloud instance events. Look for unexplained panics or network-service resets and for later root-level commands, persistence, credential access, or outbound traffic. A crash alone is not attribution, and the absence of an application request is expected for this trigger.
If evidence supports kernel-level execution, isolate the host and rebuild it from a trusted image after collecting the evidence your response process requires. Rotate secrets exposed to root on that host, replace node and service identities, and review neighboring systems reached during the window. If evidence does not support compromise, document exposure, temporary controls, the fixed runtime, and the reason the incident was closed.
Checklist
- Map every Linux kernel package, running kernel, host role, IPv4 TCP listener, MPTCP setting, and network exposure.
- Track the exact distribution, cloud, appliance, or managed-platform advisory instead of relying on an upstream version comparison.
- Prioritize internet-facing and untrusted-network hosts, shared clusters, routing nodes, and systems with MPTCP or request migration enabled.
- Where patching is delayed, test and deploy the vendor's IPv4-options filter only after checking CIPSO, routing, and container behavior.
- Disable unused MPTCP and restart existing MPTCP listeners, while treating that change only as risk reduction.
- Install a supported fixed kernel, reboot or replace the node, verify `uname -r`, and prevent rollback to vulnerable images.
- Preserve kernel, crash, network, and host evidence, and rebuild plus rotate host-readable secrets if execution is suspected.
Sources
- Red Hat RHSB-2026-016: affected products, exposure, mitigation, and update status open_in_new
- Red Hat CVE-2026-98432 record: impact, scoring, and product statement open_in_new
- Anthropic Research: demonstrated Linux remote-root chain and exploit boundary open_in_new
- Ubuntu CVE-2026-98432: kernel-package status and upstream fix reference open_in_new
- AlmaLinux: exposure details, testing builds, MPTCP scope, and temporary controls open_in_new
- Linux kernel advisory record: race analysis and stable-branch commits open_in_new
- Linux upstream fix: defer IPv4 socket-option frees through an RCU grace period open_in_new
Continue Reading
Kubeflow Pipeline Archives Put Memory Limits Before Authorization
CVE-2026-118761 lets reachable pipeline uploads exhaust API-server memory before namespace authorization. Upgrade to 2.18.0 and bound every layer.
Signal K Path Traversal Turns Read Access Into Server Command Execution
A Signal K resource flaw can expose its JWT secret and lead to command execution. Upgrade, replace old trust, and review persistent providers.
Boundary SSRF Turns A Project Role Into Controller-Network Access
A Boundary flaw lets project credential managers make controllers reach internal endpoints. Patch, review role grants, and investigate outbound requests.