Signal K Path Traversal Turns Read Access Into Server Command Execution
A Signal K resource flaw can expose its JWT secret and lead to command execution. Upgrade, replace old trust, and review persistent providers.
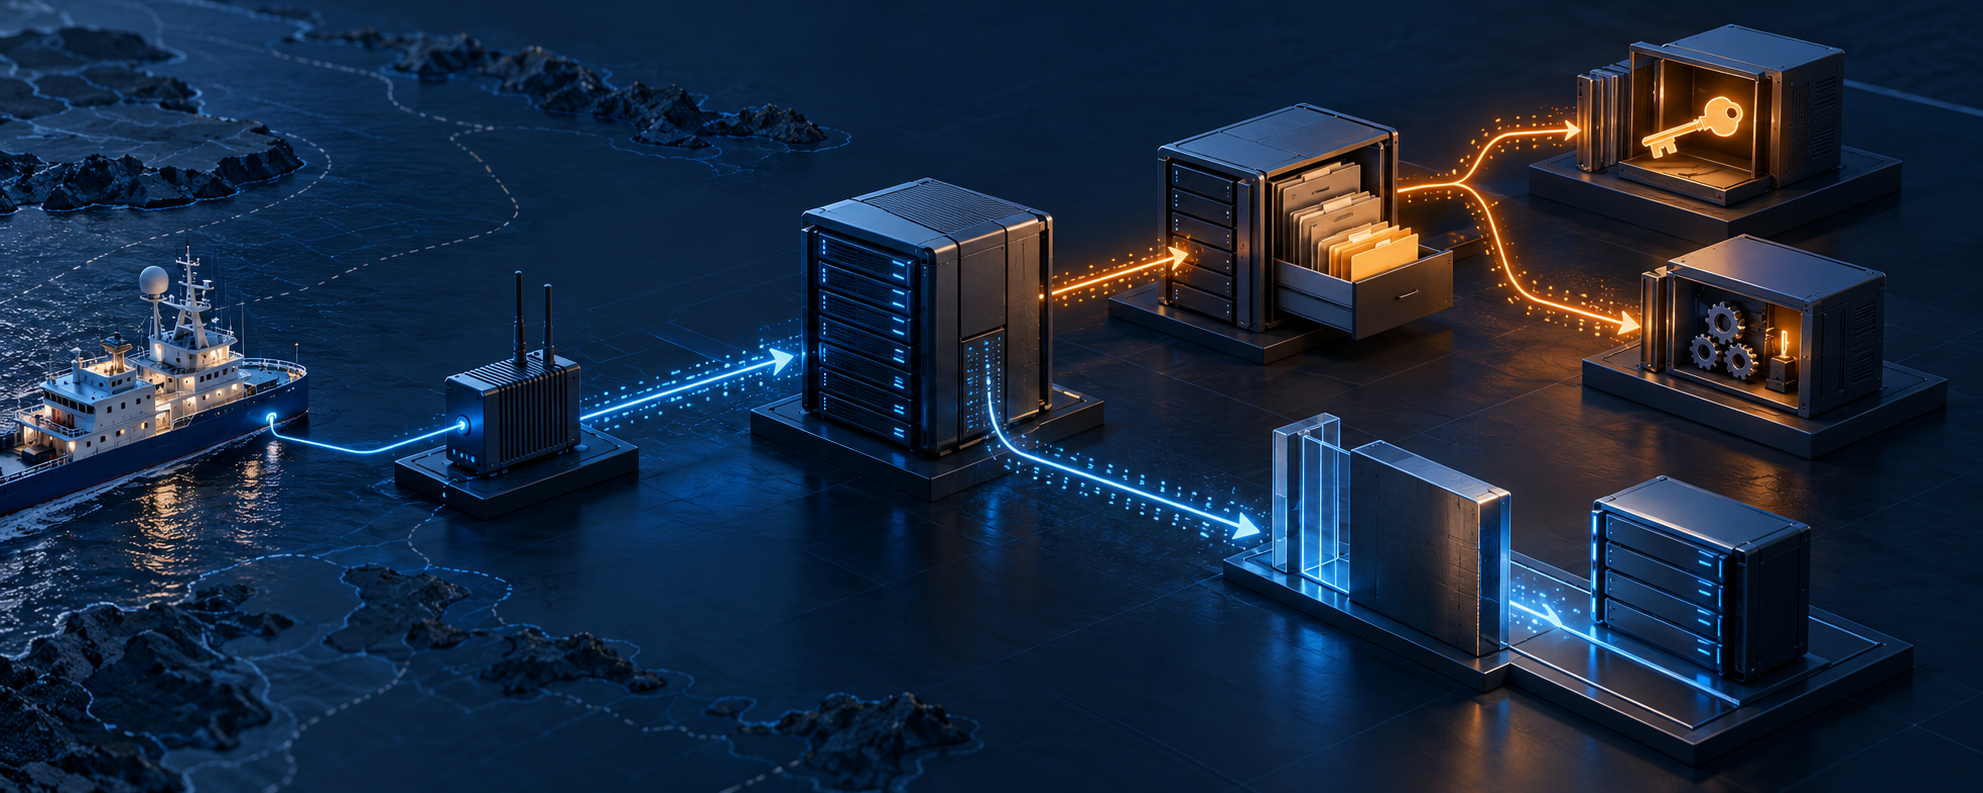
Signal K Server 2.34.0 closes a critical path-traversal chain in its resources and application-data handling. On an affected server, a crafted resource identifier can escape the intended storage directory. A read can reach the server's security configuration, expose the secret used to sign JSON Web Tokens, and let an attacker forge an administrator token. The advisory then demonstrates an administrator-only provider endpoint that starts a shell command and saves the provider for later restarts.
The shortest unauthenticated chain depends on `allow_readonly=true`, a supported setting that gives guests access to Signal K data and web apps. With the default setting off, a read-only account is required. That distinction affects exposure, but it does not make an older server safe. Operators should upgrade Signal K Server to 2.34.0 or later and the standalone resources provider to 1.5.3 or later, replace the old signing trust, inspect provider and file changes, and keep marine telemetry servers away from untrusted wireless and internet-facing paths.
Key Takeaways
- check_circle The reviewed advisory affects Signal K Server 2.0.0 through 2.33.x and the standalone `@signalk/resources-provider` package 1.0.0 through 1.5.2.
- check_circle Signal K Server 2.34.0 and resources-provider 1.5.3 are the fixed boundaries published by the project.
- check_circle When anonymous read access is enabled, the resource read can be reached without a login; otherwise any valid read-only token can satisfy the first prerequisite.
- check_circle The demonstrated chain moves from file read to signing-secret disclosure, forged administrator access, and an Execute provider that runs with the Signal K process account.
- check_circle Upgrading closes the path, but operators must separately distrust tokens signed by an exposed key and investigate persistent provider or file changes.
- check_circle The project advisory does not report malicious exploitation in the wild, so response should be driven by exposure and evidence rather than an unsupported claim of compromise.
What The October 30 Review Confirms
Signal K published its project advisory on October 18, and GitHub reviewed it and added it to the public Advisory Database on October 30. The reviewed record assigns a critical 9.8 CVSS 3.1 score. It lists `signalk-server` versions from 2.0.0 up to, but not including, 2.34.0 and `@signalk/resources-provider` versions from 1.0.0 up to, but not including, 1.5.3 as affected.
The issue is a storage-boundary failure, not a weakness in the Signal K protocol itself. The v2 resources API accepted a client-controlled resource identifier and passed it into file-store operations. Joining that value to the resource directory did not prove that the resolved file remained under the intended root. Encoded parent-directory segments could therefore reach JSON files elsewhere in the server configuration tree.
The corrective commit applies the rule in several places rather than filtering one URL. It rejects empty identifiers, dot segments, path separators, and NUL characters; resolves file paths and checks the parent directory; validates custom collection and provider names; and constrains application IDs and user identifiers in application-data storage. That breadth matters because read, write, and delete operations can otherwise become different routes to the same filesystem mistake.
How A Resource Read Becomes Administrator Access
Before 2.34.0, the server kept its JWT signing secret in `security.json`. The advisory shows that a traversal read can retrieve that JSON file along with password hashes. Possession of the signing secret changes the problem from unauthorized file access to broken authentication: the attacker can create an HS256 token that the server accepts as belonging to the administrator identity.
The final step uses intended administrator functionality. Signal K supports data providers, including an Execute provider that starts a configured shell command. The advisory demonstrates a forged administrator token being used to create that provider. Creation starts the command, and the provider is written to `settings.json`, so it can run again after a restart. The result is command execution with the operating-system privileges of the Signal K process, not automatic control of every device on the vessel.
Release 2.34.0 both confines resource paths and moves the signing secret outside `security.json`. Those are complementary defenses. Input validation stops the immediate traversal, while separating key material reduces the consequence if an application-readable configuration file is exposed later. Neither change erases evidence or invalidates an attacker-created provider on a server that was already reached.
Anonymous Exposure Is A Setting, Not The Whole Boundary
Signal K's current security documentation says `allow_readonly` is off by default for new secured installations. Administrators can enable it so guest crew, displays, and web apps can read navigation data without individual accounts. Existing installations preserve the value already written to their security configuration, including systems created when anonymous read behavior differed.
With `allow_readonly=true`, the advisory's resource GET reaches the vulnerable file operation without a login. With it off, an attacker needs any read-only user token. Write and delete paths still depend on their corresponding permissions. Inventory the actual setting and exposed identities rather than assuming a default from the current documentation represents an upgraded or long-lived server.
Network placement can widen the audience. Signal K warns that local services may be visible to every device on a shared Wi-Fi network, including marina networks, and that port forwarding can expose a server to the public internet. A vessel gateway, chart display, maintenance laptop, or guest device can all share routes that were treated as trusted. Record listeners, reverse proxies, tunnels, wireless segments, and forwarded ports before deciding the issue was reachable only from a safe console.
Upgrade, Then Replace The Old Trust
Upgrade the complete Signal K Server deployment to 2.34.0 or later. If the resources provider is deployed or packaged separately, prove that it is 1.5.3 or later as well. Check the runtime that actually starts after maintenance, not only a downloaded package, image tag, or lock file. Container users should identify the immutable image digest and replace old replicas rather than updating one short-lived container by hand.
Treat the previous JWT secret as exposed when the vulnerable resources API was reachable by an untrusted principal. The project documentation notes that deleting `security.json` resets access to the administration interface, but that is a recovery mechanism, not a low-risk rotation command. Plan a supported signing-key replacement that invalidates existing tokens, preserves only reviewed user and ACL data, and accounts for devices or integrations that must enroll again. Test that process away from navigation-critical operations.
Changing passwords alone is incomplete because a forged token is validated with the signing secret, not with the password hash at the moment of use. Rotate other credentials only where investigation shows they were stored in reachable JSON, passed to a malicious provider, or accessible to the Signal K process. Broad, unsequenced rotation can interrupt data collection without removing a saved command provider.
Investigate Files, Tokens, Providers, And Child Processes
Preserve the configuration directory, application-data tree, resource stores, `settings.json`, server logs, reverse-proxy logs, and container or service metadata before cleanup. Search request paths for encoded slashes, parent-directory segments, unusual resource types, and repeated reads that end at JSON files. A missing HTTP log entry does not prove safety if a proxy normalizes or omits encoded paths.
Compare providers and plugin settings with a known-good export. Give special attention to new or changed Execute providers, commands, endpoints, startup behavior, and modifications that appeared during the exposure window. At the host layer, review child processes launched by the Signal K service account, created files, scheduled tasks, shell histories where applicable, outbound connections, and changes outside the normal configuration root.
Token review has limits after a signing key is stolen because a forged token can look structurally valid. Correlate administrator actions with known users, source addresses, device enrollment, and change windows. If execution evidence exists, contain the host, preserve volatile evidence where feasible, rebuild from trusted media or an image, restore only reviewed configuration, and rotate secrets the process could read.
Make The Marine Server A Smaller Trust Domain
Run Signal K as a dedicated, non-root operating-system identity with write access only to required storage. Keep secrets for unrelated services out of its home and configuration paths. Limit outbound network access to documented integrations so command execution cannot freely reach management services, cloud metadata, or every device network.
Disable anonymous read access where guest displays do not require it. Where it is operationally necessary, keep the service on a controlled vessel network and avoid exposing its administration or resource APIs through public forwarding. TLS protects credentials and telemetry in transit, but it does not repair a path traversal accepted by the application itself.
Finally, separate navigation continuity from server administration. Keep a tested way to operate essential instruments if the Signal K host must be isolated or rebuilt. A security response that requires preserving a compromised server because every display depends on it is a design failure that segmentation, configuration backups, and recovery drills can prevent.
Checklist
- Inventory every Signal K Server and standalone resources-provider version, including containers and embedded appliances.
- Upgrade Signal K Server to 2.34.0 or later and resources-provider to 1.5.3 or later, then verify the running instances.
- Record `allow_readonly`, user and device tokens, public listeners, port forwards, tunnels, and shared wireless reachability.
- Preserve configuration, resource, application-data, provider, HTTP, service, and host evidence before removing suspicious state.
- Replace the prior JWT signing trust and invalidate old sessions through a tested, supported recovery plan.
- Review Execute providers, `settings.json`, child processes, created files, outbound connections, and service-account access.
- Run the server with least privilege and restrict administration, filesystem scope, and egress to required destinations.
Sources
- Signal K project advisory: affected packages, exploit chain, impact, and fixed versions open_in_new
- GitHub Advisory Database: reviewed GHSA-4xm8-rg9h-jhq2 record open_in_new
- Signal K Server 2.34.0 release notes and signing-secret change open_in_new
- Signal K corrective commit: path confinement and identifier validation open_in_new
- Signal K security documentation: anonymous read, users, devices, and recovery behavior open_in_new
- Signal K breaking changes: anonymous-read default and existing-installation behavior open_in_new
- Signal K specification: transport, server, and marine data-system context open_in_new
Continue Reading
Polymarket Script Compromise Turns Browser Sessions Into Wallet Authority
A hijacked performance script used active Polymarket sessions to sell positions and move funds. Audit browser vendors, sessions, DNS, CSP, and integrity.
Kubeflow Pipeline Archives Put Memory Limits Before Authorization
CVE-2026-118761 lets reachable pipeline uploads exhaust API-server memory before namespace authorization. Upgrade to 2.18.0 and bound every layer.
Linux IPv4 Race Makes Kernel Patching A Network Perimeter Issue
CVE-2026-98432 reaches Linux kernel memory through IPv4 TCP handshakes. Track distro fixes, test packet filters, reboot, and prove the runtime.