Tailscale 1.104.4 Fixes A Trusted-Peer Path To Root
Tailscale 1.104.4 fixes SSH and Serve flaws that let authorized peers cross local privilege boundaries. Patch affected nodes and tighten forwarding policy.
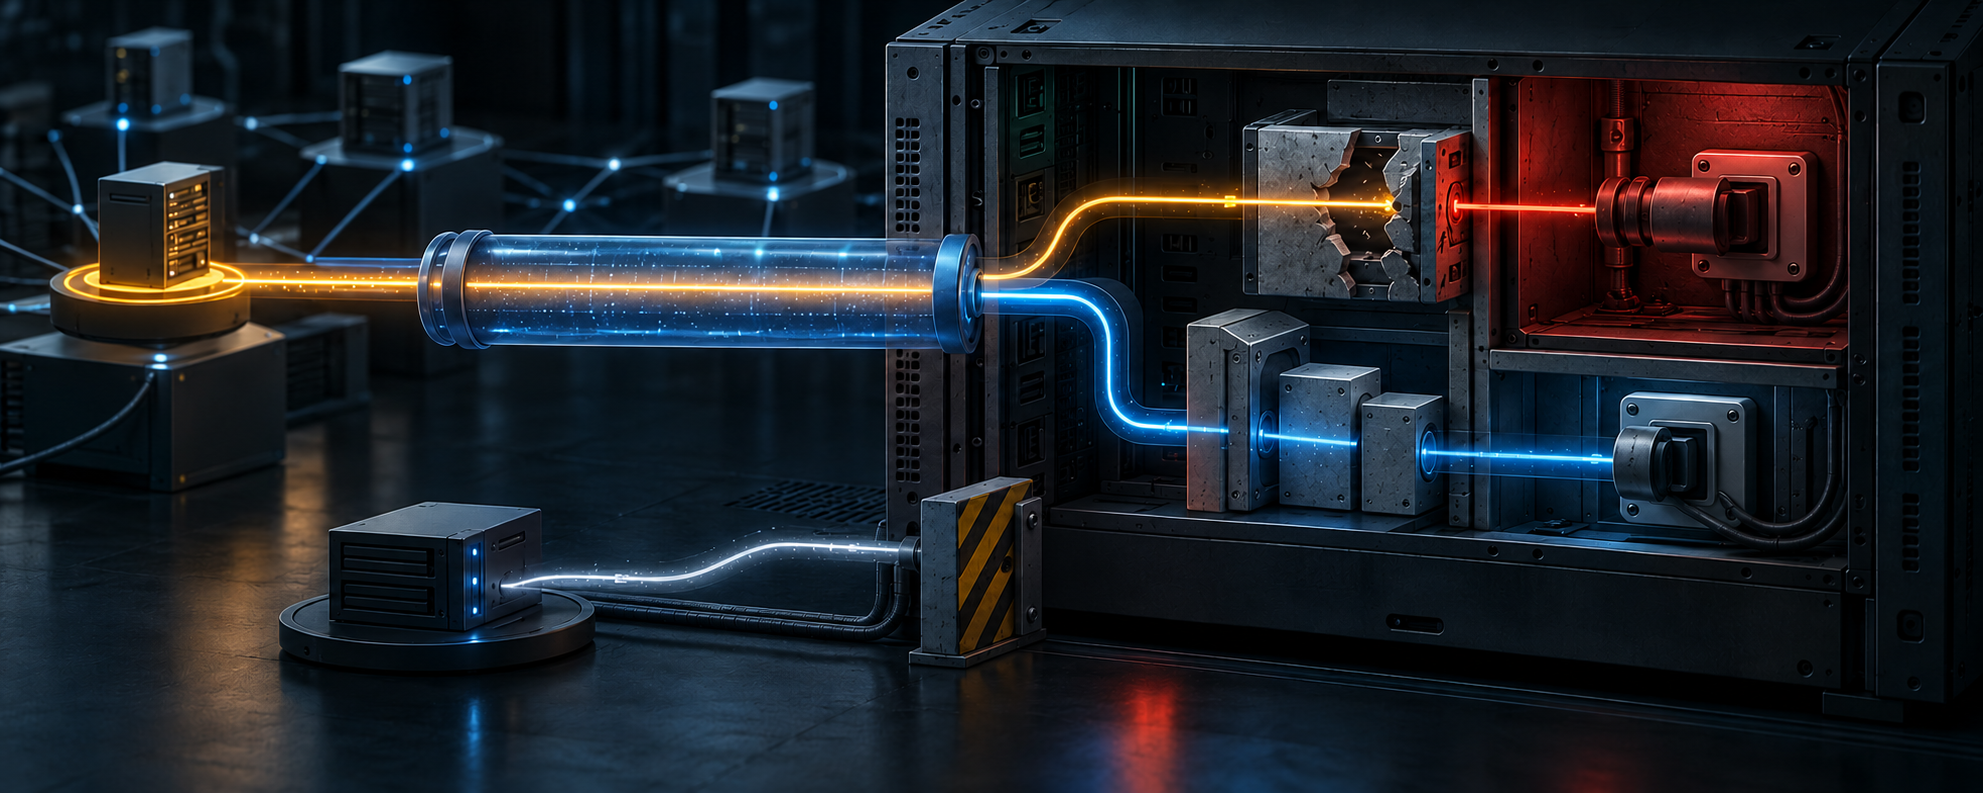
Tailscale has released version 1.104.4 after confirming four security issues in Tailscale SSH and Tailscale Serve. The most consequential flaw let an authenticated peer with policy-authorized SSH forwarding reach root-only Unix sockets, including the Docker socket or the tailscaled local API. Separate issues could expose privileged Serve backends, exhaust tailscaled memory, or mix application capability headers between concurrent HTTP/2 streams. The fixes change operations to run in the authenticated user's context, revalidate socket targets, bound session memory, and keep capabilities in per-request state.
These are post-authentication privilege-boundary failures, not a path for an arbitrary internet host to join a tailnet. Exploitation requires an existing foothold on an authorized peer or specific local operator access, plus the affected feature and policy conditions. Operators should still treat the update as urgent because a compromised workstation or workload that was deliberately allowed to reach production could gain authority beyond its configured Unix user. Upgrade every affected node to 1.104.4 or later, verify the running daemon version, review SSH and Serve policy, and investigate high-consequence sockets where the conditions existed.
Key Takeaways
- check_circle Tailscale says all four confirmed issues in security bulletins TS-2026-014 through TS-2026-017 are fixed in version 1.104.4.
- check_circle The SSH privilege escalation requires a peer that is already authorized by tailnet policy to open an SSH session and use local or remote forwarding; it is not unauthenticated internet access or self-spreading malware.
- check_circle TS-2026-014 allowed root-context Unix socket forwarding, while TS-2026-016 exposed privileged sockets through certain Serve configurations and mutable backend paths.
- check_circle TS-2026-015 let an authenticated Tailscale SSH session retain unbounded memory allocations until tailscaled could be killed, disrupting all Tailscale connectivity on the node.
- check_circle TS-2026-017 affected Serve nodes with TLS and multiple mounts using different application capabilities, where concurrent HTTP/2 streams could receive the wrong capability values.
- check_circle Patching closes the code paths, but operators must separately decide whether an already authorized peer was compromised and whether root-only sockets or privileged responses were reachable.
The Fix Arrived After A Compressed Disclosure Window
Tailscale says concerns began circulating on October 23, it received the research report on the morning of October 24, and the report was published about two hours later. The company issued an initial investigation update on October 26, then shipped 1.104.4 and a detailed findings-and-fixes report with four bulletins. That sequence matters because early claims included more findings than the vendor ultimately classified as separate customer-facing vulnerabilities.
The canonical scope is now narrower and more useful. Tailscale confirmed privilege and availability bugs in the released Tailscale SSH and Serve features. It says a reported issue in Conn25 affected a pre-production app-connector implementation that has not shipped. It also says two Serve and Funnel findings described intended behavior that depends on local administrator access or an explicit setting designed to expose Serve beyond the tailnet. Those points should not be merged into the patch scope for deployed stable app connectors.
The public materials do not describe a mass compromise or identify in-the-wild exploitation. That absence is not proof that no affected path was used. The practical response is configuration-led: identify nodes where the required features and permissions existed, patch them, and preserve evidence before assuming that a trusted peer remained trustworthy throughout the exposure period.
Serve And Session Bugs Have Different Exposure Tests
TS-2026-016 concerns Tailscale Serve configurations that proxy to Unix sockets. One path let a TCP forward send raw bytes to the tailscaled local API using root privileges. Another checked a symbolic link only when the configuration loaded, allowing a local user who could later replace the backend path to redirect a request to a privileged socket. The fixed version blocks forwards to the daemon socket and revalidates the backend target for every dial.
TS-2026-015 is an availability issue on nodes running the Tailscale SSH server. An authenticated peer could send continuous window-change messages or append environment variables and make session allocations persist after disconnection. Unbounded growth could trigger the operating system's out-of-memory response and kill tailscaled. Because the daemon owns all Tailscale networking state on the host, the impact is broader than one failed SSH session.
TS-2026-017 applies to a different Serve shape: TLS enabled, at least two mounts on the same node, different capability requirements, and concurrent streams sharing one HTTP/2 connection. A shared context could carry Tailscale-App-Capabilities from one request into another mount. Applications that trusted that header for authorization might return a privileged response to the wrong peer. The fix derives capabilities from per-request state. Inventory must therefore distinguish SSH, Unix-backed Serve, and multi-mount HTTP/2 Serve rather than marking every Tailscale node equally exposed.
Patch Proof Must Reach The Running Daemon
Start with nodes that expose production administration, container runtimes, hypervisors, build systems, storage, or identity services. Confirm whether Tailscale SSH is enabled, whether policy permits forwarding, whether Serve references Unix sockets, and whether TLS Serve mounts make authorization decisions from application capability headers. A client merely participating in a tailnet is not enough to satisfy these conditions, but unsupported assumptions about feature state are not evidence.
Upgrade to 1.104.4 or later through the platform's supported channel, then verify the version reported by the running daemon after restart. Package repositories, appliance firmware, containers, NAS integrations, and embedded distributions can lag upstream. Record the node identity, previous and current versions, restart time, image digest or package source, and a functional connection test. A downloaded installer or changed manifest does not prove that an old process stopped.
For containers and immutable hosts, replace the image rather than modifying a running layer. Verify that orchestration did not preserve an older digest and that every replica rolled. For managed desktops, query fleet state instead of relying on automatic update settings. If a platform cannot yet deliver 1.104.4, disable the affected feature, remove forwarding permission, or take the node out of sensitive access paths until a supported build is available.
Trusted Peers Still Need A Least-Privilege Interior
A mesh VPN can strongly authenticate a device and still hand too much authority to the software that serves the next protocol. The confirmed bugs did not defeat WireGuard encryption or let an unauthenticated outsider bypass the tailnet policy file. They showed that identity and reachability controls are insufficient when a privileged daemon performs post-authentication operations on behalf of a less-privileged user.
Keep SSH rules narrow by source, destination, and local user. Use check mode for sensitive systems so a stolen but still enrolled device is not the only factor for a high-consequence connection. Treat forwarding as a separate permission, test policy assertions, and avoid placing container-runtime or administrative sockets behind generic proxy targets. Production nodes should not share Serve mounts with unrelated authorization requirements when separation is practical.
Maintain a current security contact and fleet inventory so a vendor bulletin can be mapped to real nodes quickly. Device approval, posture checks, short-lived enrollment, and rapid removal of lost devices reduce the foothold set. None replaces a fixed build, but together they make an authorized-peer compromise less likely to become a root-level lateral movement path.
Checklist
- Inventory nodes with Tailscale SSH, SSH forwarding, Unix-backed Serve, or TLS Serve mounts that use application capability headers.
- Upgrade affected nodes to Tailscale 1.104.4 or later and verify the running daemon version, restart time, package source, and container digest where applicable.
- Disable SSH forwarding with TS_SSH_DISABLE_FORWARDING=1 and restart tailscaled on any exposed node that cannot yet receive the fixed build.
- Reduce SSH policy by source, destination, local user, and forwarding need; use check mode for production and other high-consequence targets.
- Review authorized peers, identity events, SSH records, tailscaled restarts, out-of-memory events, Serve configuration, and policy changes for the relevant period.
- Investigate Docker, containerd, CRI, tailscaled, and other root-only sockets wherever an affected forwarding or Serve path existed.
- Rebuild hosts and rotate node or downstream credentials when privileged-socket access is plausible and the available logs cannot establish integrity.
Sources
- Tailscale: findings, response timeline, fixed release, and confirmed scope open_in_new
- Tailscale security bulletins TS-2026-014 through TS-2026-017 open_in_new
- Cyberdione Labs: original Tailworm research and upstream response open_in_new
- Tailscale Docs: SSH architecture, revocation, and check mode open_in_new
- Tailscale Docs: policy syntax and SSH policy tests open_in_new
- Tailscale Docs: tailnet security and notification practices open_in_new
Continue Reading
Mattermost Agents Flaw Turns An Admin Click Into Server Code Execution
A Mattermost Agents flaw can turn a crafted channel post and an admin click into plugin replacement and server code execution. Patch supported lines now.
SilverFox Turns WhatsApp Attachments Into Signed Remote Control
SilverFox spreads document lures through WhatsApp and installs a signed management agent. Hunt enrollment, certificates, sessions, and host evidence.
GoAhead TLS Flaws Make The Firmware Build The Security Boundary
GoAhead 6.1.1 fixes backend-specific TLS flaws affecting revocation, chain depth, and forward secrecy. Device owners must identify firmware builds.