SilverFox Turns WhatsApp Attachments Into Signed Remote Control
SilverFox spreads document lures through WhatsApp and installs a signed management agent. Hunt enrollment, certificates, sessions, and host evidence.
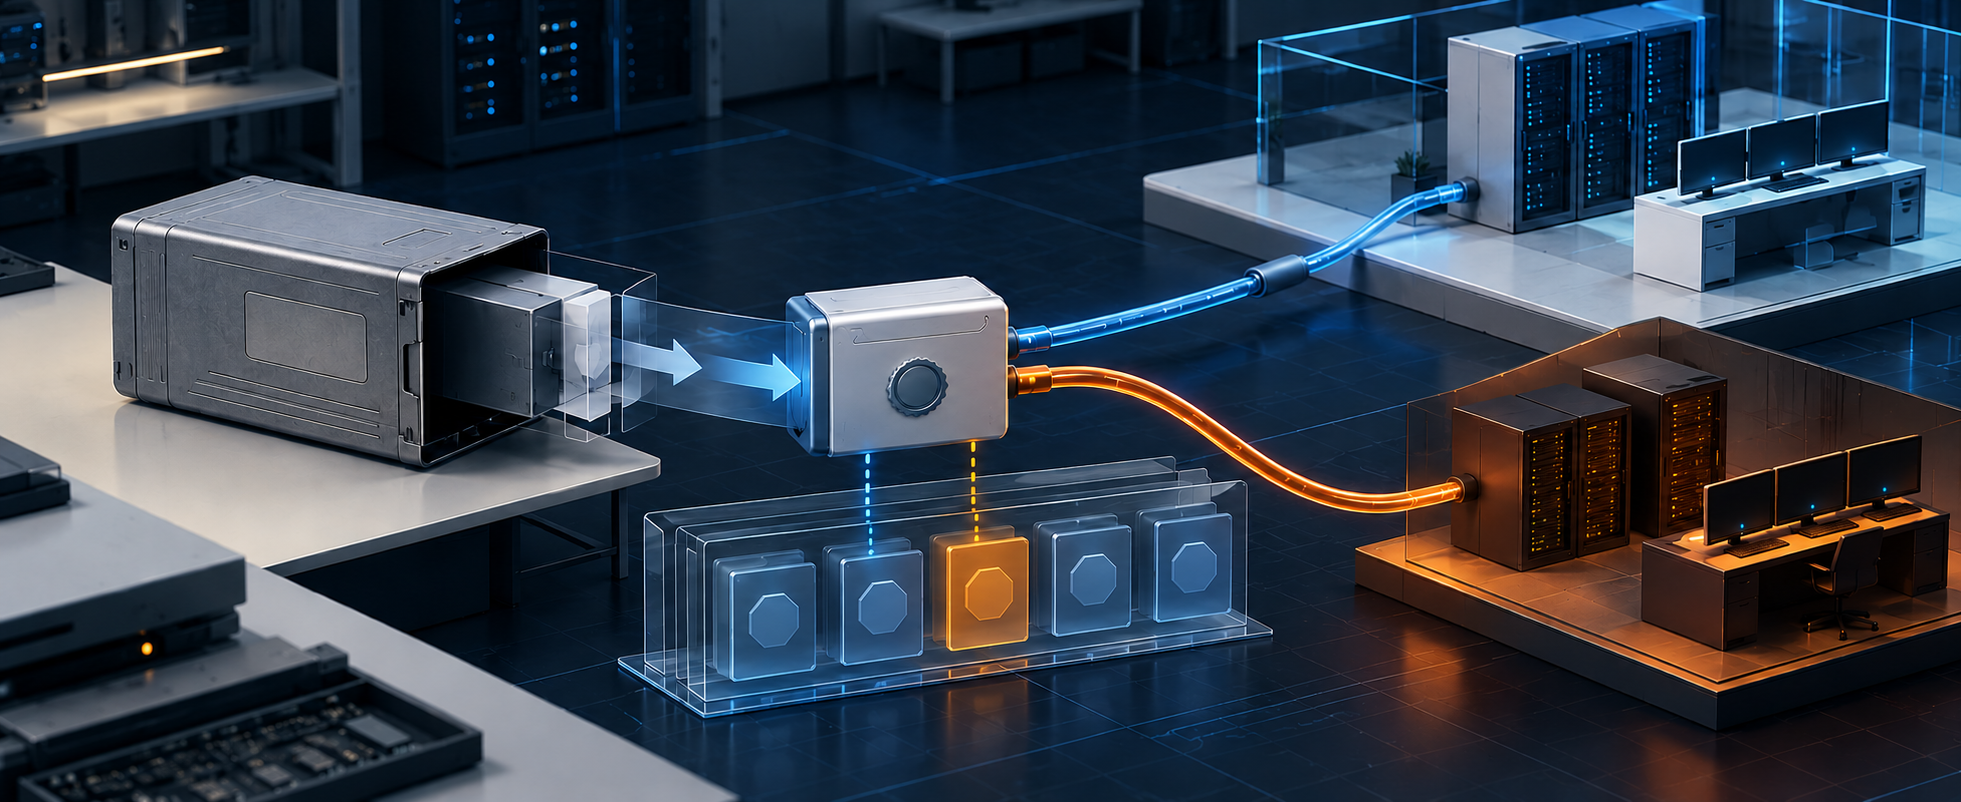
Singapore's SingCERT says it has received multiple reports of malicious files spreading through compromised WhatsApp accounts. People who opened the attachments later found similar files sent to their contacts without authorization. The advisory connects those cases to host indicators from a MyCERT investigation of SilverFox, a campaign that disguises Windows virtual disk images as business documents and installs a genuine, vendor-signed ManageEngine UEMS Agent enrolled to attacker-controlled infrastructure.
The signed agent is not the safety signal it appears to be. MyCERT detonated the chain in a lab and observed the agent install as a service, trust forged management certificates, connect to a hostile server over TCP port 8383, and provide remote command, file-transfer, and application-control capability. Defenders must evaluate where an agent is enrolled, how it arrived, and which trust anchors were added. Removing an unfamiliar WhatsApp Web session or uninstalling the agent alone does not establish that the device is clean.
Key Takeaways
- check_circle SingCERT confirmed reports of malicious attachments distributed through compromised WhatsApp accounts and subsequent unauthorized forwarding to victims' contacts.
- check_circle MyCERT analysed three SilverFox builds and observed a genuine ManageEngine UEMS Agent 6.0.3 enroll to attacker-controlled servers over TCP port 8383.
- check_circle The lure uses password-protected archives and document-like names around VHDX or ISO files, reducing normal download warnings after the image is mounted.
- check_circle A valid vendor signature does not make the enrollment trustworthy; the decisive evidence is the agent's server address, installation context, added certificates, and surrounding artifacts.
- check_circle MyCERT recommends treating positive findings as full compromise, isolating and rebuilding the host rather than relying on agent uninstallation.
- check_circle WhatsApp recovery and linked-device review are necessary containment steps, but endpoint, credential, banking, and corporate-resource exposure must be scoped separately.
What The Two Government Advisories Establish
SingCERT published its advisory on October 28 after receiving multiple reports of malicious files sent through compromised WhatsApp accounts. It says victims who downloaded and opened the files later discovered that similar attachments had been sent to their contacts without their knowledge. The agency warns that the malware can expose credentials, hijack active WhatsApp Web sessions, monitor activity including online banking, and provide unauthorized device access.
MyCERT's October 24 alert supplies the deeper host analysis. It examined three campaign builds, fully detonated two of them in isolated environments, and observed a genuine ManageEngine UEMS Agent enroll to attacker-operated management servers. Kaspersky shared a register of 151 initial archive hashes seen in September and October, and MyCERT found two of its analysed containers in that set. MyCERT uses Kaspersky's SilverFox name, also tracked as Void Arachne, but says no confirmed attribution to a named threat group has been established.
The records should not be collapsed into one claim. MyCERT says the delivery channel was not consistently established across all analysed samples. SingCERT separately confirms WhatsApp distribution in reported cases and points defenders to MyCERT's matching host indicators. The sound conclusion is that WhatsApp is an observed delivery and propagation channel for this malware pattern, not that every SilverFox archive in the 151-hash register was sent through WhatsApp.
How A Document Lure Becomes A Management Agent
The initial archive is often password-protected and contains a single file named to resemble a PDF or banking document. The file is actually a Windows virtual disk image, such as VHDX or ISO. When mounted, files inside the image do not inherit the normal Mark of the Web flag from the downloaded container, which reduces SmartScreen and Protected View friction. The victim still has to mount the image and run the embedded program, so this is execution through deception rather than a no-click messaging exploit.
Inside the image, MyCERT found a legitimate signed crash-reporting executable beside an unsigned malicious library. The signed program loads the library by name. That side-loading step elevates privileges, creates `C:\kouren` or `C:\cool`, retrieves another archive, and runs `msiexec` to install the genuine ManageEngine UEMS Agent 6.0.3 silently.
The installation also adds forged `ManageEngineCA` root certificates to the Windows trusted store. The agent then enrolls to the attacker's UEMS server and beacons over TCP port 8383. This is the important security boundary: the same signed management software can be legitimate when enrolled to an organization's own console and hostile when enrolled to someone else's. Binary reputation cannot answer which controller has authority.
Why WhatsApp Propagation Changes The Trust Model
A file from a known contact usually gets more trust than an email attachment from an unknown sender. SingCERT's reports show why that shortcut fails. Once a device or active WhatsApp Web session is controlled, the attacker can send the same lure from a real account into existing conversations. Recipients see familiar identity and message history even though the sender did not authorize the file.
Verification must therefore leave the compromised channel. Replying inside the same chat only asks the possibly controlled account to confirm itself. Call the sender using a known number, speak in person, or use another independently protected channel. Treat urgent instructions to open an archive on a computer, mount a disk image, or review a banking document as high-risk even when the message comes from a colleague or family member.
Organizations should also decide whether unmanaged consumer messaging belongs in business document exchange. If staff use WhatsApp for customer statements, payroll material, invoices, or support files, security controls designed for corporate email and managed file transfer may never inspect the archive. A policy that merely says not to open strange files will lose to a real contact sending a plausible work document.
Hunt The Enrollment, Not Just The Signature
MyCERT's most useful indicators are contextual. Look for `C:\kouren` and `C:\cool`; `msiexec` installing `UEMSAgent.msi` with `SERVER_ROOT_CRT=` or `DS_ROOT_CRT=` parameters; an unexpected UEMS Agent installation; `ManageEngineCA` certificates in the trusted root store; and outbound connections to the published backend addresses on TCP port 8383. Build 3 also created `C:\cool\Agentinstalllog.txt`.
Do not globally classify the UEMS Agent MSI as malware. MyCERT says the package is a genuine vendor file, and ManageEngine's own documentation confirms that `UEMSAgent.msi`, `UEMSAgent.mst`, and `DCAgentServerInfo.json` are normal parts of agent deployment. The malicious state comes from the side-loaded installer chain, forged trust material, unapproved server configuration, and attacker-controlled enrollment.
Inventory every UEMS or Endpoint Central agent and compare its controller address, certificate chain, install time, service creation, deployment owner, and change ticket with the organization's approved management architecture. A signed binary in the correct program directory is not enough. Any agent that points outside the approved server set, or appears on a host that should not have endpoint-management software, deserves immediate isolation.
Contain The Device And The Messaging Account Separately
For a host with matching indicators, MyCERT recommends full-compromise handling: isolate it, preserve evidence, and rebuild from clean media. Uninstalling the agent is insufficient because the service uses persistence and tamper-protection flags, and a normal uninstall does not remove the forged root certificates. The actor may also have used remote control to add other tools, copy data, or change settings outside the UEMS installation path.
Scope credentials from a clean device. Review corporate SSO, email, file shares, VPN, password managers, browser sessions, banking, e-wallets, and payment apps that were accessible while the agent was active. Rotate credentials based on evidence and authority, not only on which passwords were typed after the suspicious attachment opened. Review authentication and transaction records for the full likely exposure window.
Handle WhatsApp as a second workstream. From a known-clean phone, review linked devices and log out anything unfamiliar. WhatsApp's guidance says re-registering with the six-digit SMS code logs out other devices when the account itself is compromised. Enable two-step verification, warn contacts through a trusted channel, preserve the lure and timestamps, and do not access WhatsApp Web again from the suspect computer until it has been rebuilt.
Controls That Break This Chain Earlier
Block or restrict mounting VHD, VHDX, ISO, and IMG files from user-writable locations. Control execution of `msiexec`, command interpreters, archive utilities, and unsigned libraries in user contexts. Alert when an endpoint-management agent appears outside the approved deployment process, when new root certificates are added, or when management traffic goes to an unapproved internet controller.
Application allowlisting must account for legitimate tools used illegitimately. CISA, NSA, FBI, MS-ISAC, and partners have long warned that remote-management software can provide persistence and command-and-control while blending into normal administration. A policy that trusts a publisher everywhere may permit the exact signed agent an attacker wants. Combine signer rules with approved paths, deployment provenance, controller destinations, and behavior-chain detection.
Finally, keep messaging response practical. Make it easy to report a file without opening it, provide a separate verification route, and publish a short playbook for people who already ran the attachment. Fast reporting preserves logs and limits propagation. Shame and vague awareness slogans push victims to quietly delete the message while the attacker retains the device and session.
Checklist
- Warn users not to open password-protected archives or mount VHD, VHDX, ISO, or IMG files received through chat.
- Verify unexpected business documents through a separate trusted channel, not by replying in the same conversation.
- Hunt the MyCERT paths, installer parameters, root certificates, agent enrollment, port 8383 traffic, and published indicators.
- Inventory approved UEMS and Endpoint Central agents and validate each controller, certificate chain, install time, and owner.
- Isolate and rebuild hosts with matching campaign context; do not rely on signature checks or agent uninstallation alone.
- From a clean device, review WhatsApp linked devices, recover the account if needed, enable two-step verification, and warn contacts.
- Scope corporate and financial credentials, sessions, files, and transactions reachable during the suspected control window.
Sources
- SingCERT: Advisory on Malware Campaigns Spreading Through WhatsApp open_in_new
- MyCERT: SilverFox Campaign Abuses ManageEngine UEMS Agent open_in_new
- ManageEngine: Endpoint Central Cloud agent installation open_in_new
- WhatsApp: How to recover a compromised account open_in_new
- WhatsApp: How to unlink a device open_in_new
- CISA and partners: Guide to Securing Remote Access Software open_in_new
- MITRE ATT&CK: Remote Access Tools T1219 open_in_new
Continue Reading
ServiceNow Fixes Put Admin Scripts And Plaintext Passwords In Incident Scope
ServiceNow fixed an admin sandbox escape and unintended plaintext password storage. Verify updates, review privileged scripts, and scope credential exposure.
Mattermost Agents Flaw Turns An Admin Click Into Server Code Execution
A Mattermost Agents flaw can turn a crafted channel post and an admin click into plugin replacement and server code execution. Patch supported lines now.
Tailscale 1.104.4 Fixes A Trusted-Peer Path To Root
Tailscale 1.104.4 fixes SSH and Serve flaws that let authorized peers cross local privilege boundaries. Patch affected nodes and tighten forwarding policy.